


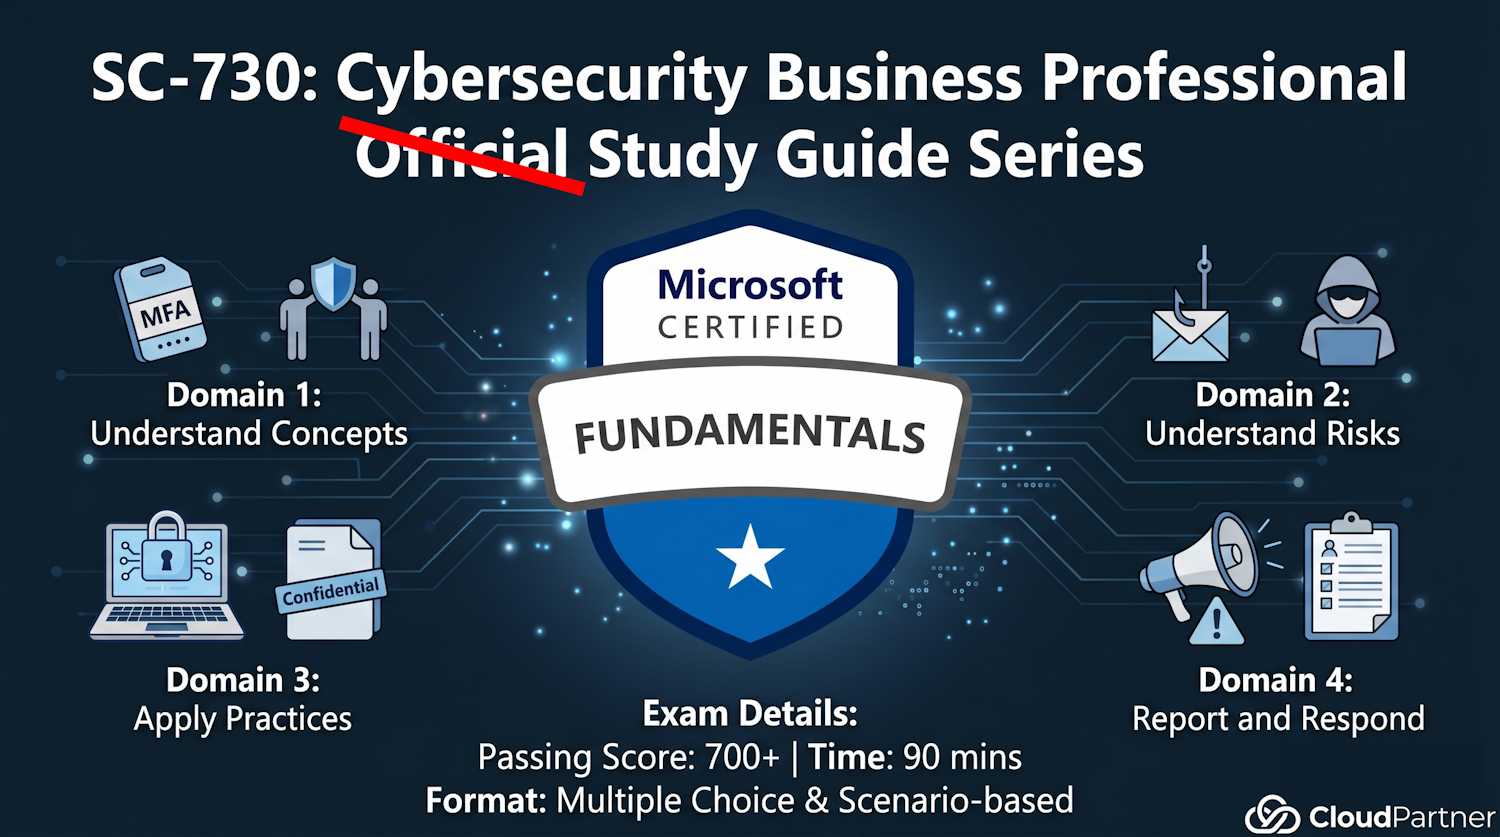
SC-730 Part 4: Report & Respond to Security Incidents (10–15%)
SC-730 Part 4: Incident Response & Reporting | Cloudpartner
SC-730 Part 4: Incident Response & Reporting | Cloudpartner
SC-730 Part 3b: Data Handling & Backups | Cloudpartner
SC-730 Part 3a: Device & Data Security | Cloudpartner
SC-730 Part 2b: Threat Detection & Email Safety | Cloudpartner
SC-730 Part 2a: Common Cybersecurity Risks | Cloudpartner
SC-730 Part 1: Cybersecurity Concepts | Cloudpartner
SC-730 Cybersecurity Business Professional Study Guide – Index | Cloudpartner
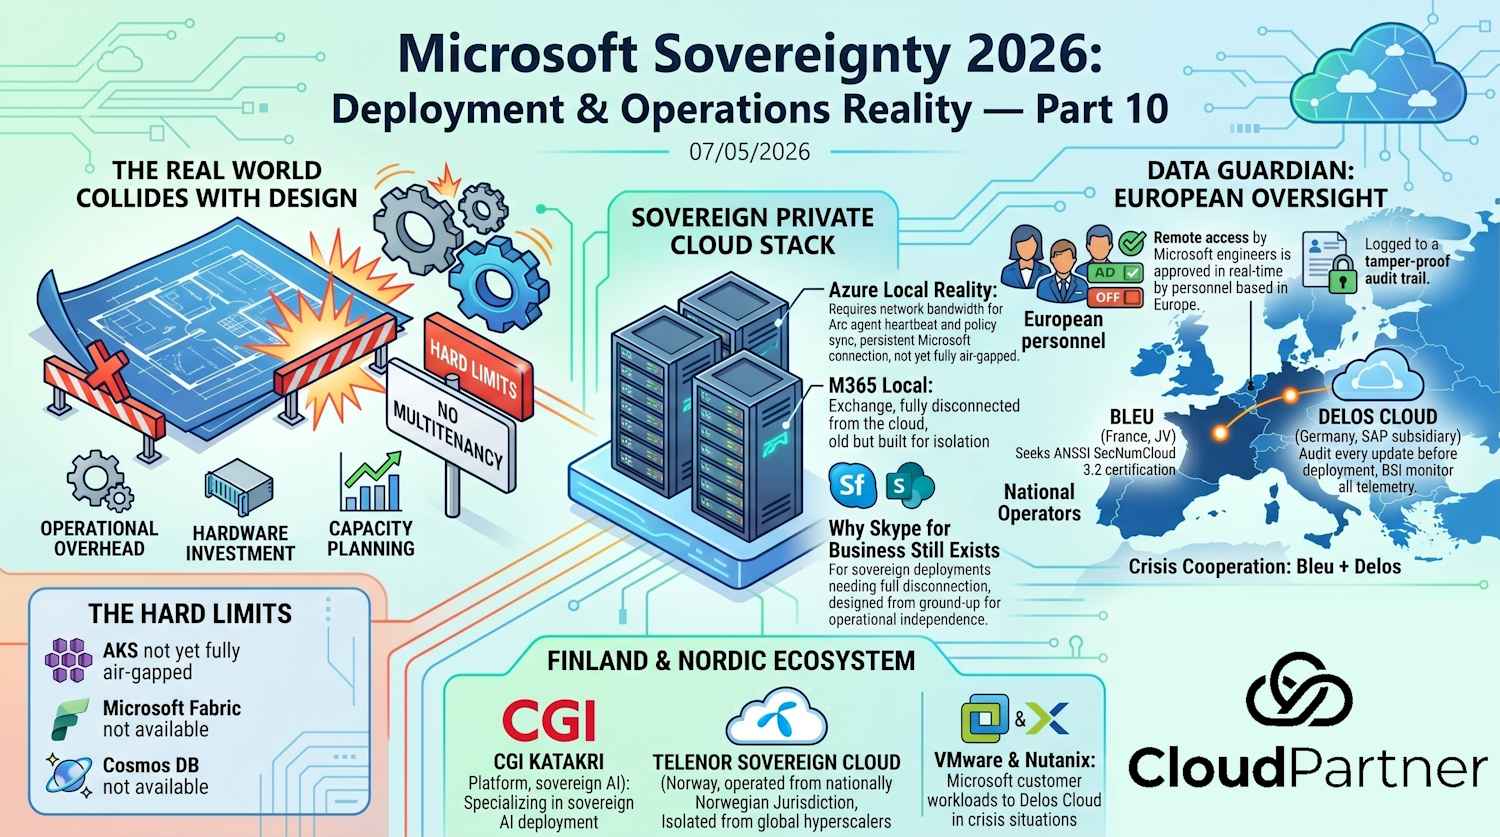
Part 10: Sovereign Private Cloud (Azure Local, M365 Local, Foundry Local), operational reality, national operators, Data Guardian enforcement, and practical decision frameworks for sovereignty deployments.
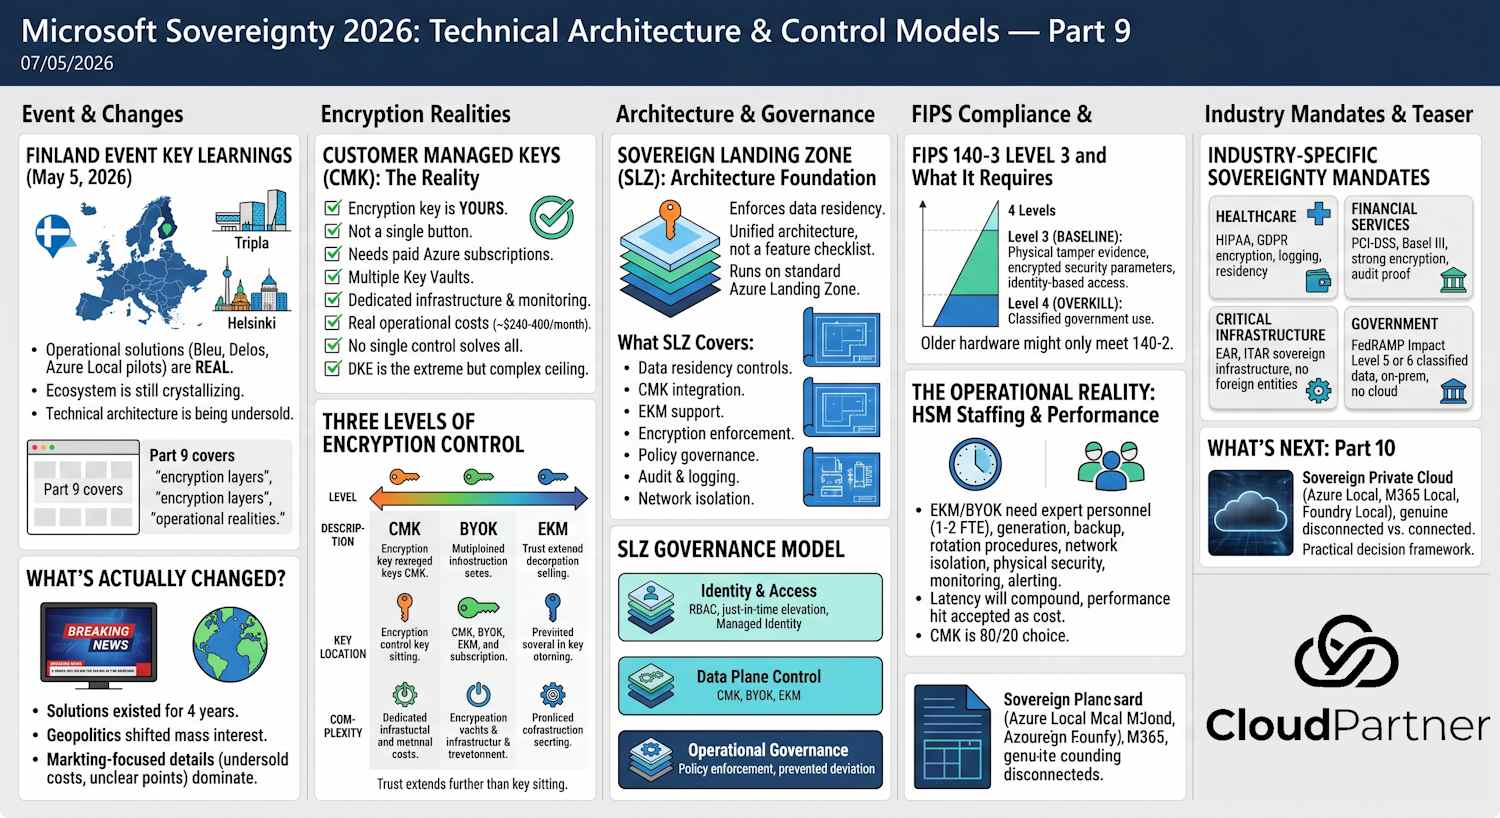
Part 9 of the Microsoft Sovereignty series. Sovereign Landing Zone architecture, Customer Managed Keys (CMK), External Key Management (EKM), and control plane governance — what they actually mean in practice, not marketing speak.
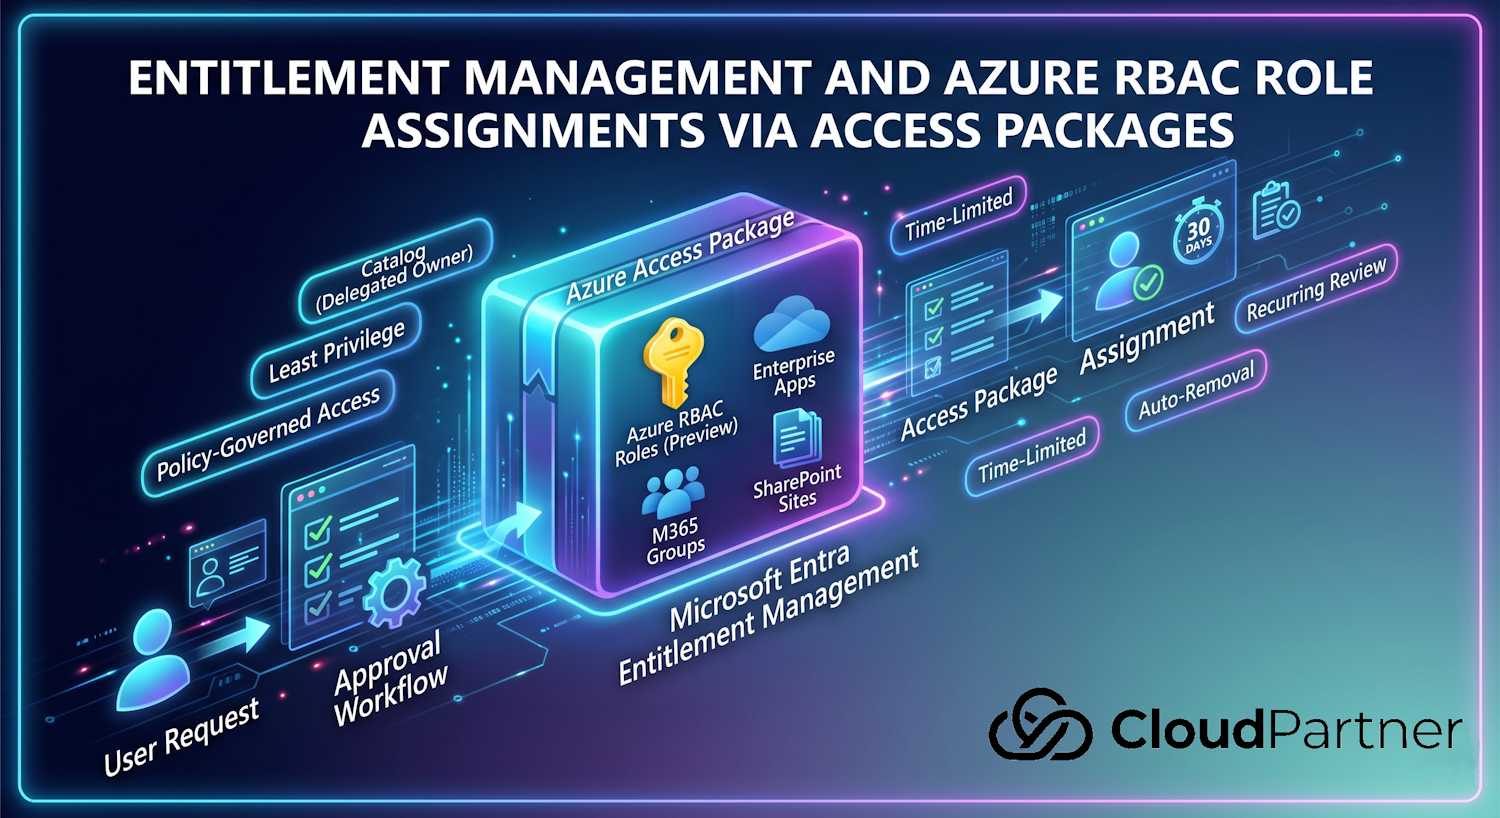
How Microsoft Entra Entitlement Management works — access packages, catalogs, and policies — and how to assign Azure RBAC roles through access packages with approval workflows, time limits, and PIM-eligible assignments.
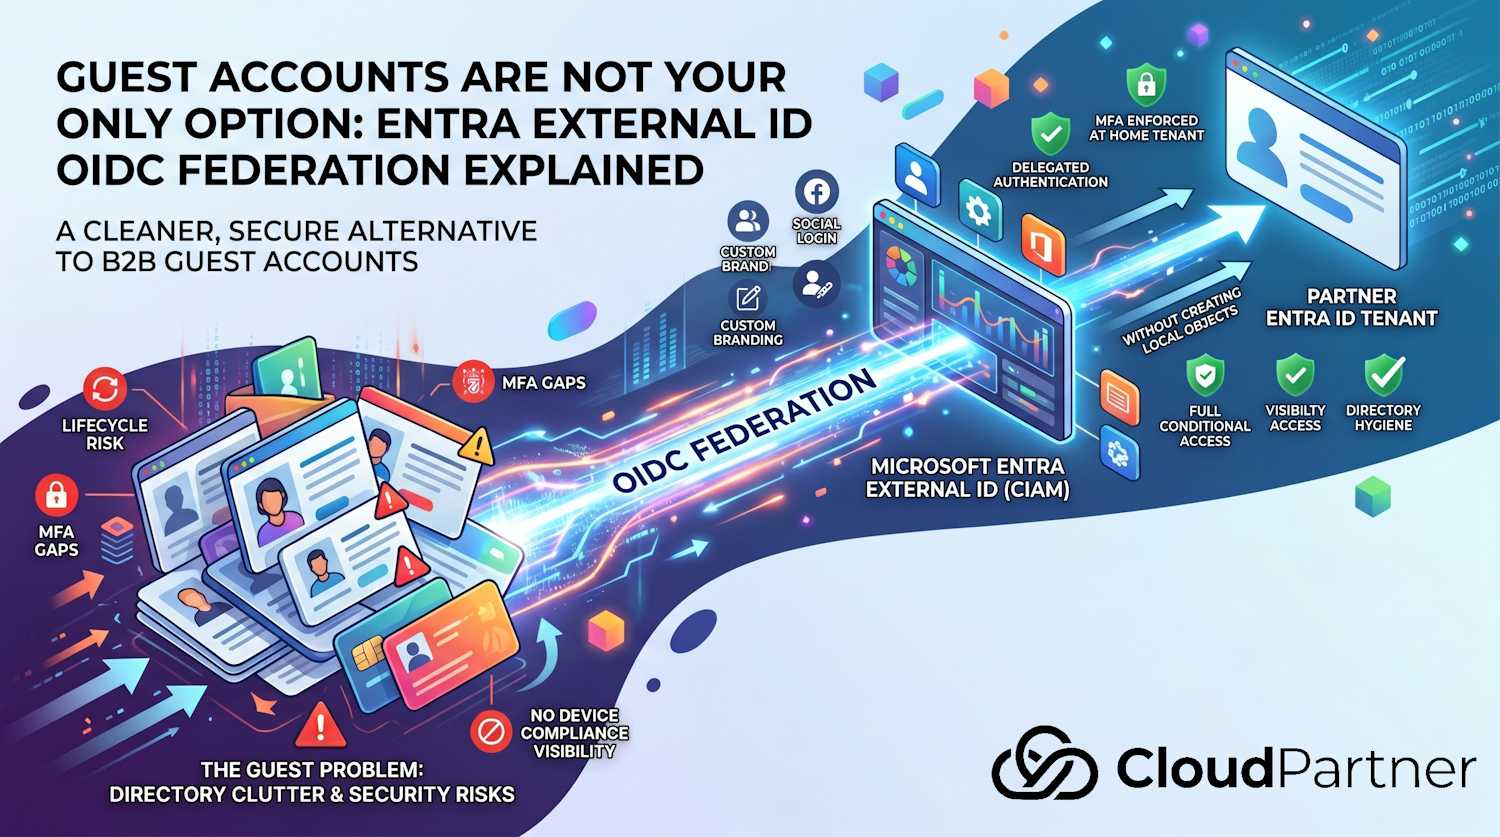
What B2B guest accounts actually do to your tenant, why they accumulate security debt, and how Entra External ID OIDC federation with another Entra ID tenant gives you a cleaner authentication model.
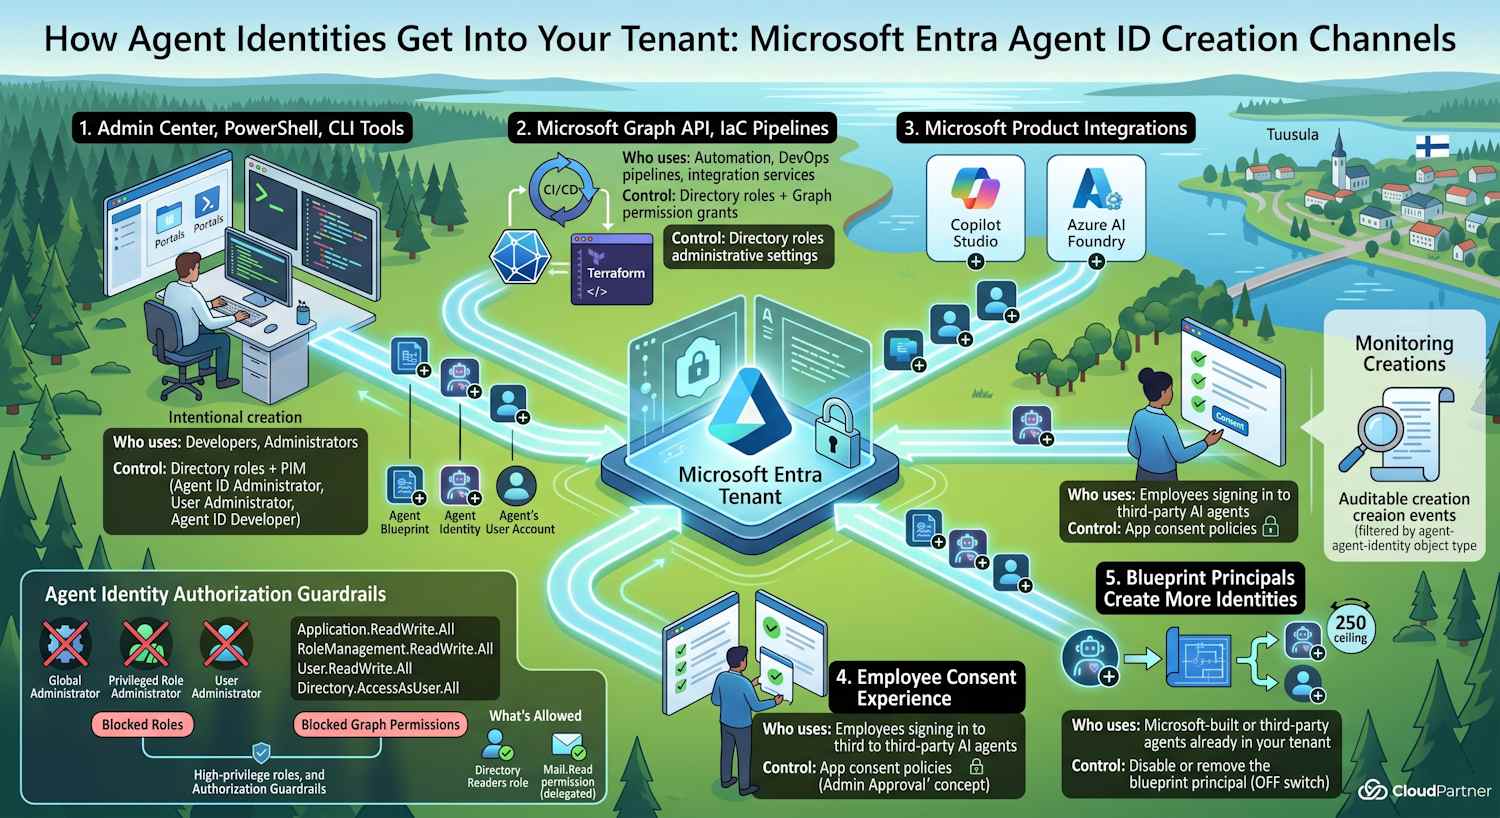
Microsoft Entra Agent ID supports multiple channels for creating agent identities — from admin tooling and Graph API to employee consent and Microsoft product integrations. Here's what they are, who controls them, and how to stay on top of what's appearing in your tenant.
How Autodesk MCP servers, Azure AI Foundry, and isolated container apps combine to give AI models governed access to CAD and BIM tools — without mixing credentials between users or relying on brittle custom integrations.
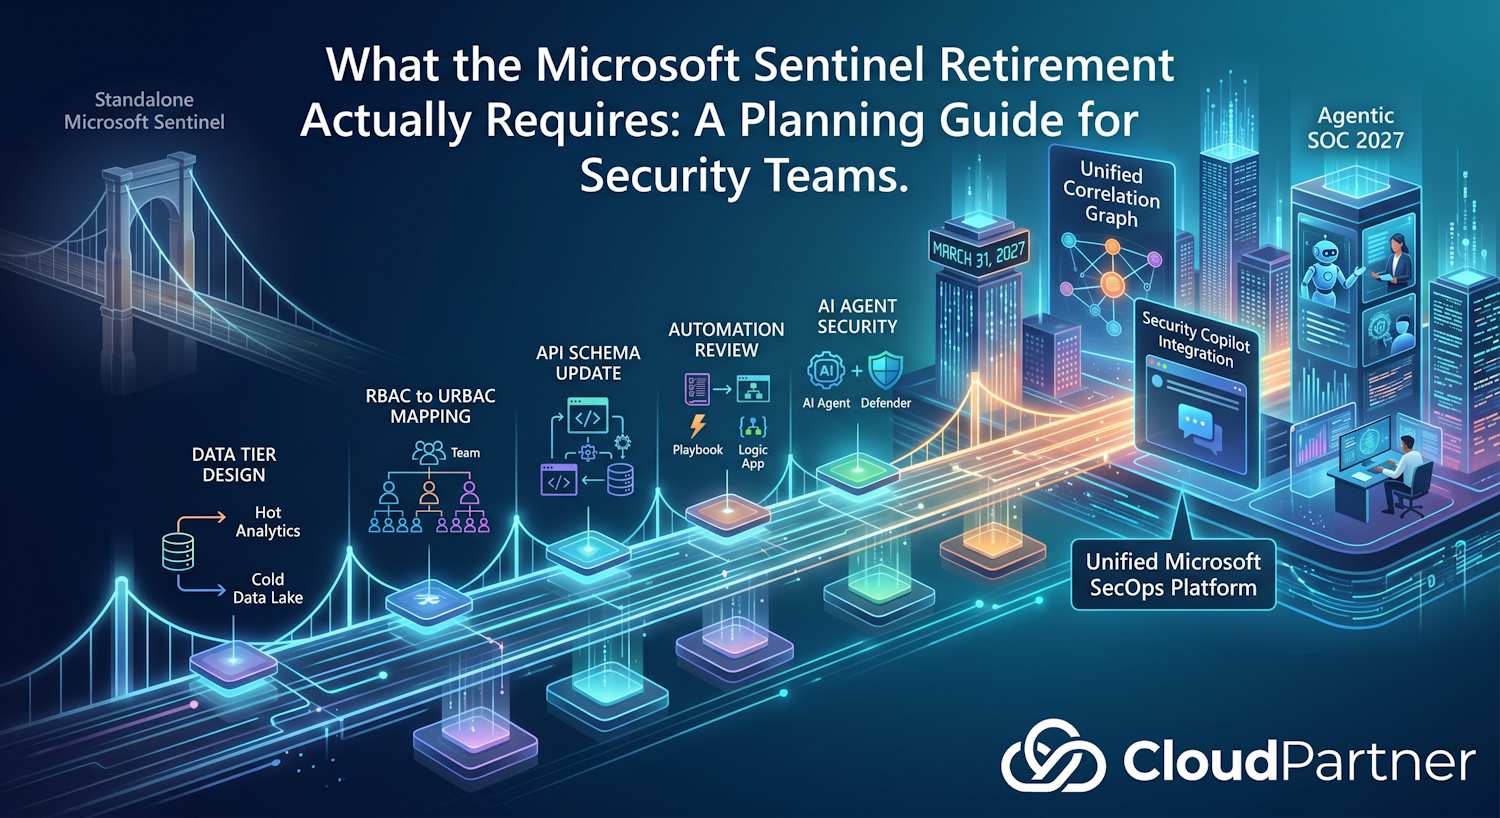
The move from standalone Microsoft Sentinel to the unified Defender portal isn't just a UI change. It's a data architecture project, a detection rethink, and the foundation for building an agentic SOC before the March 2027 deadline.
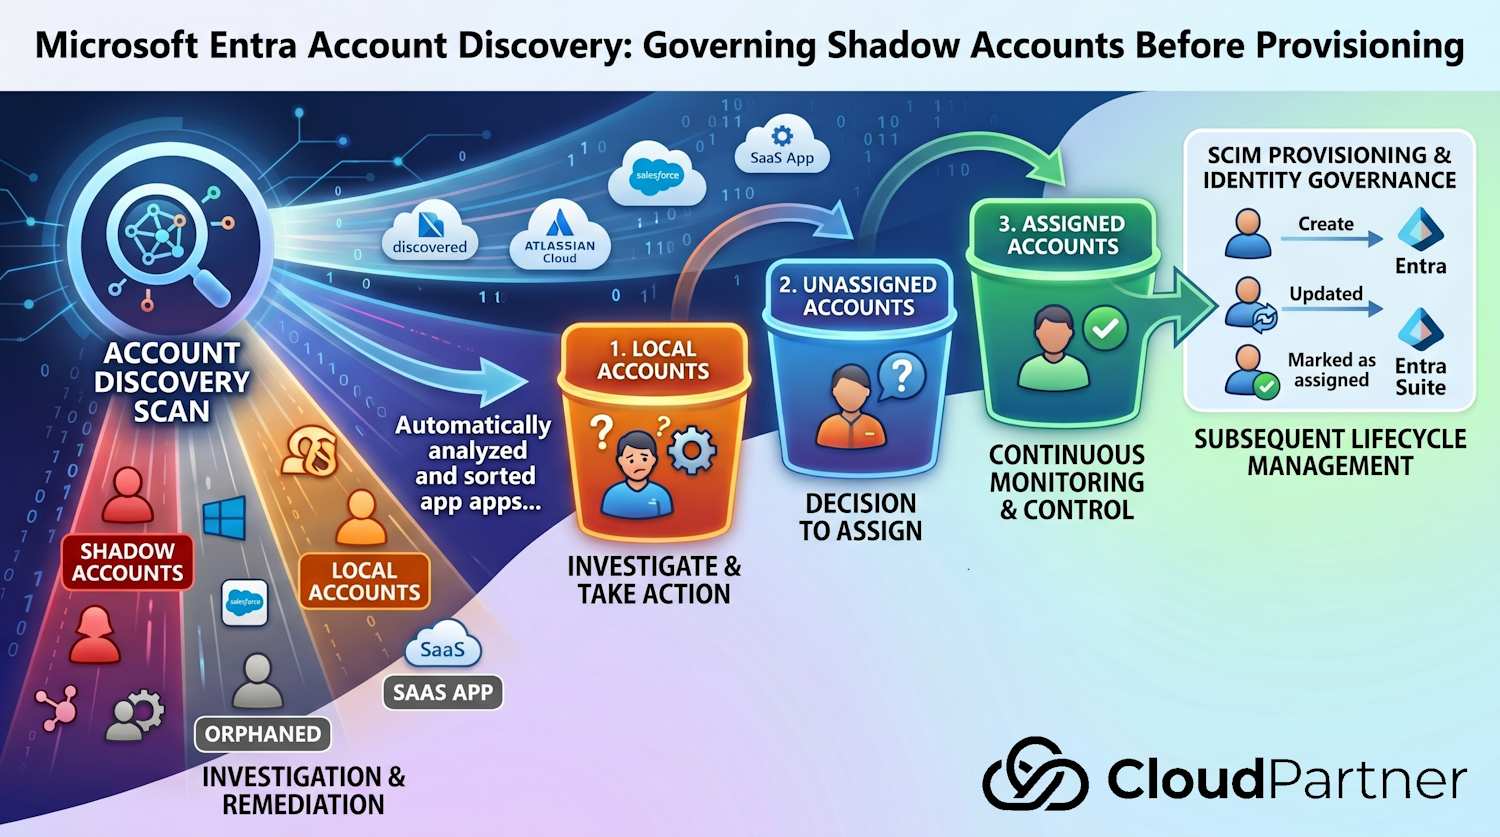
Discover how Microsoft Entra Account Discovery helps you find and govern pre-existing accounts in applications created before provisioning was configured.
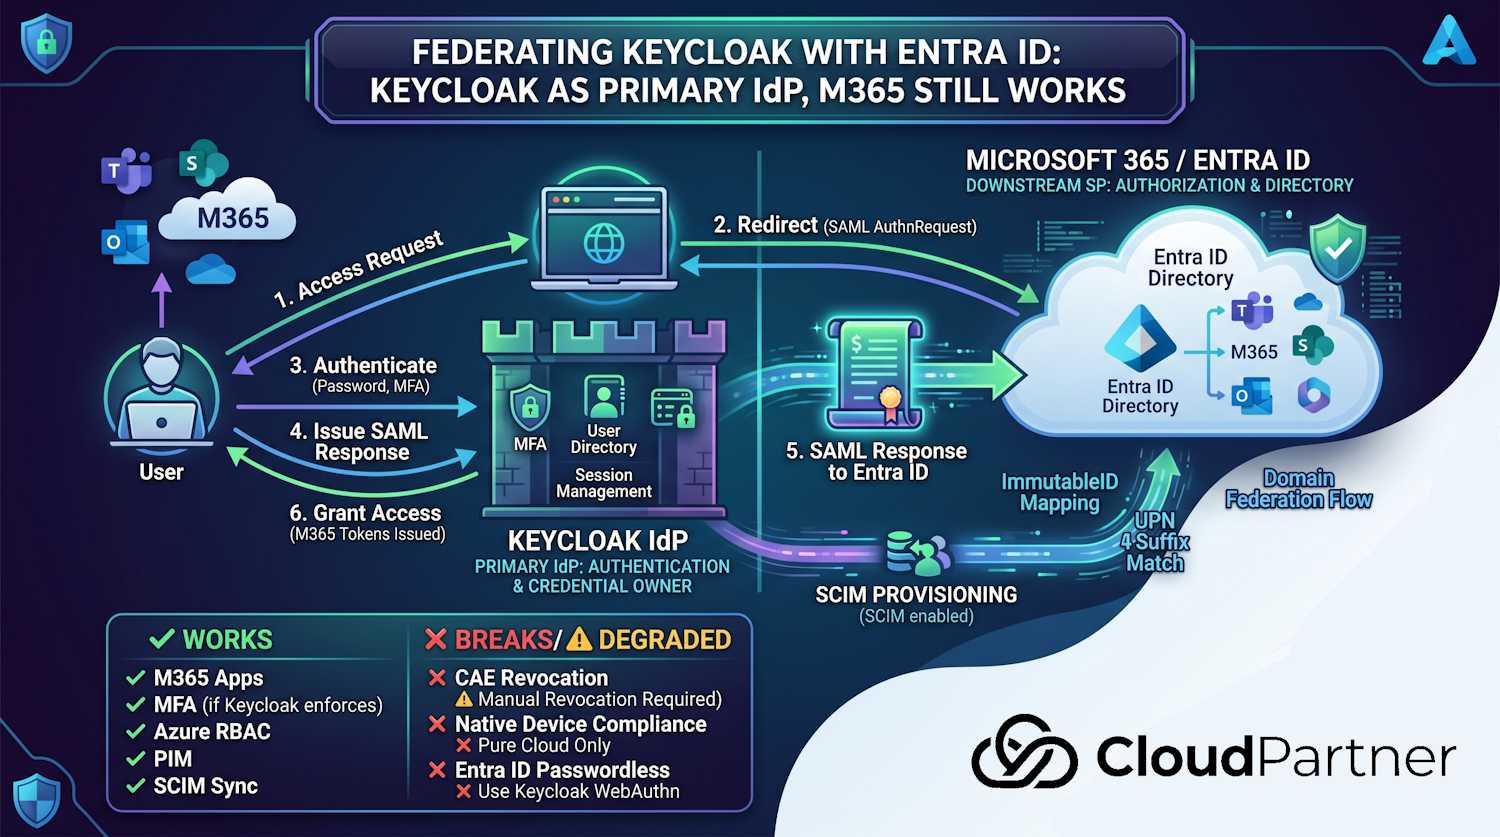
Part 5 of the EU data sovereignty series. How to federate Keycloak as your primary identity provider while keeping Microsoft 365 functional — the architecture, the configuration, and what actually breaks.
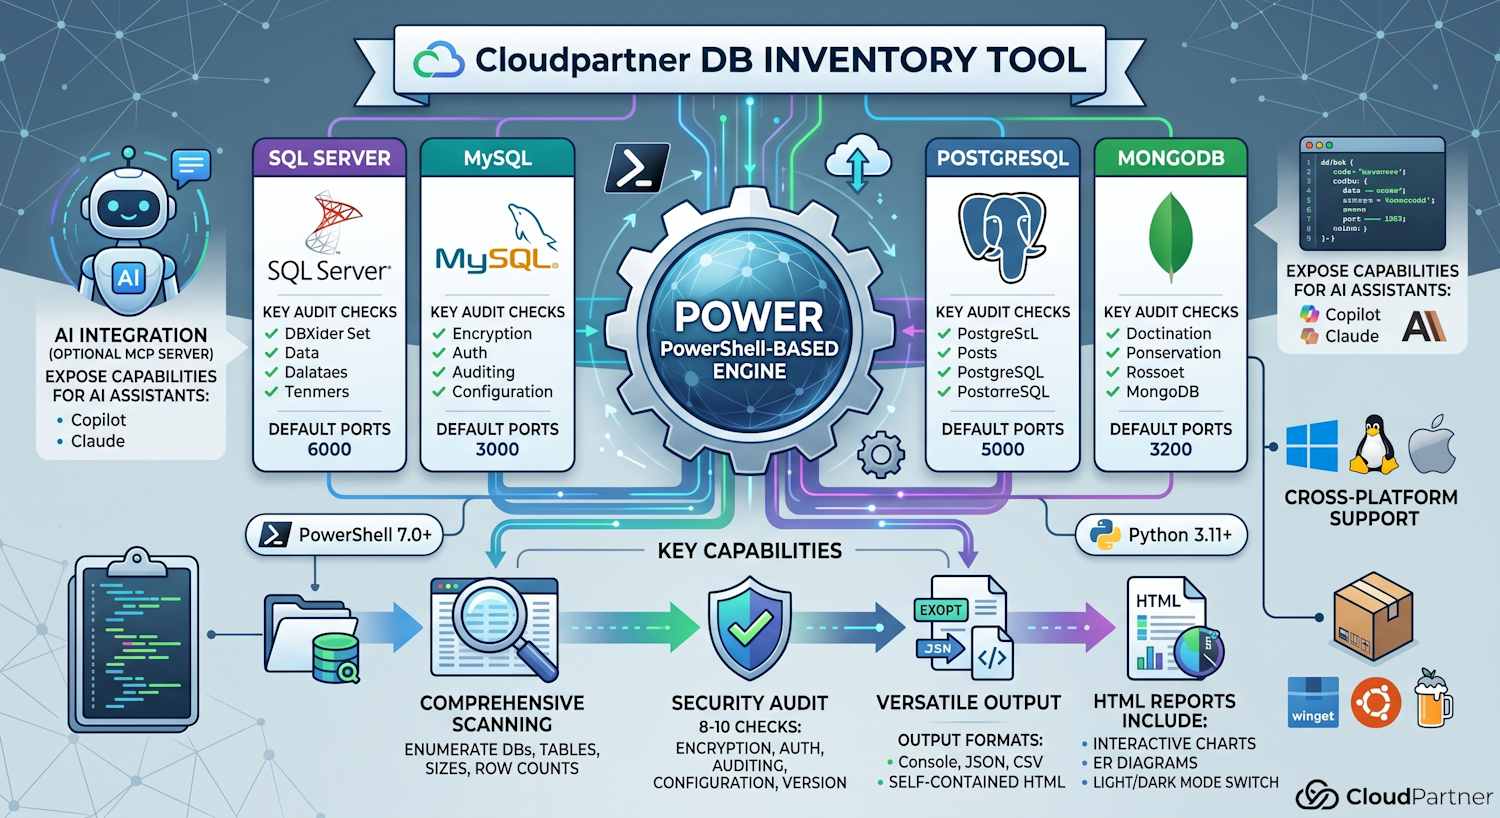
Organizations laid off their DBAs. Someone still needs to understand those schemas. I built a cross-platform PowerShell tool that visualizes database schemas, runs a 10-step security audit, and ships an MCP server so AI can help you make sense of it all.
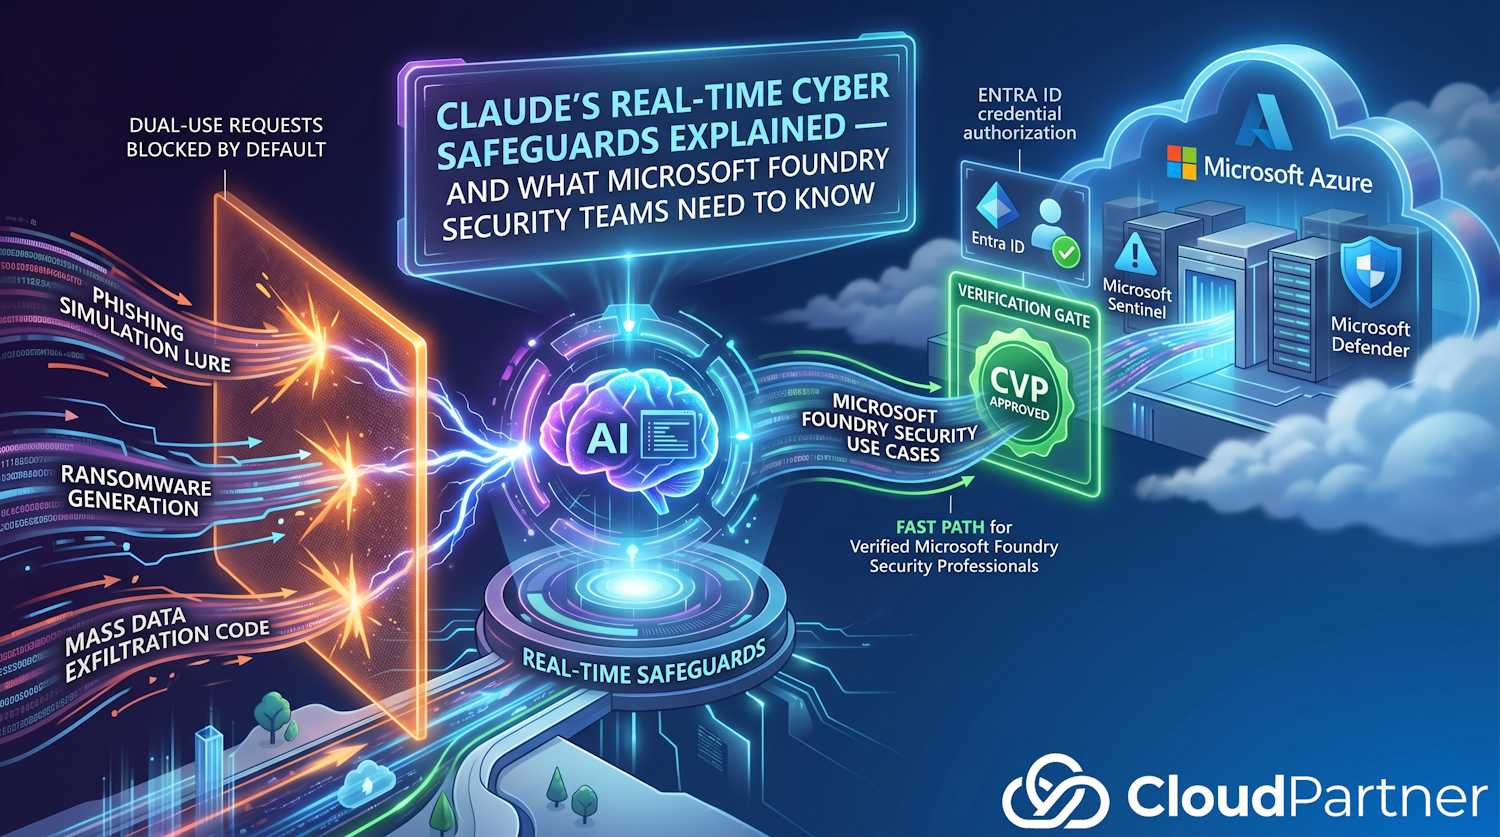
Anthropic has added real-time cyber safeguards to Claude's most capable models. Here's what they block, why the Cyber Verification Program exists, and how Microsoft Foundry users on Azure apply for legitimate security work.
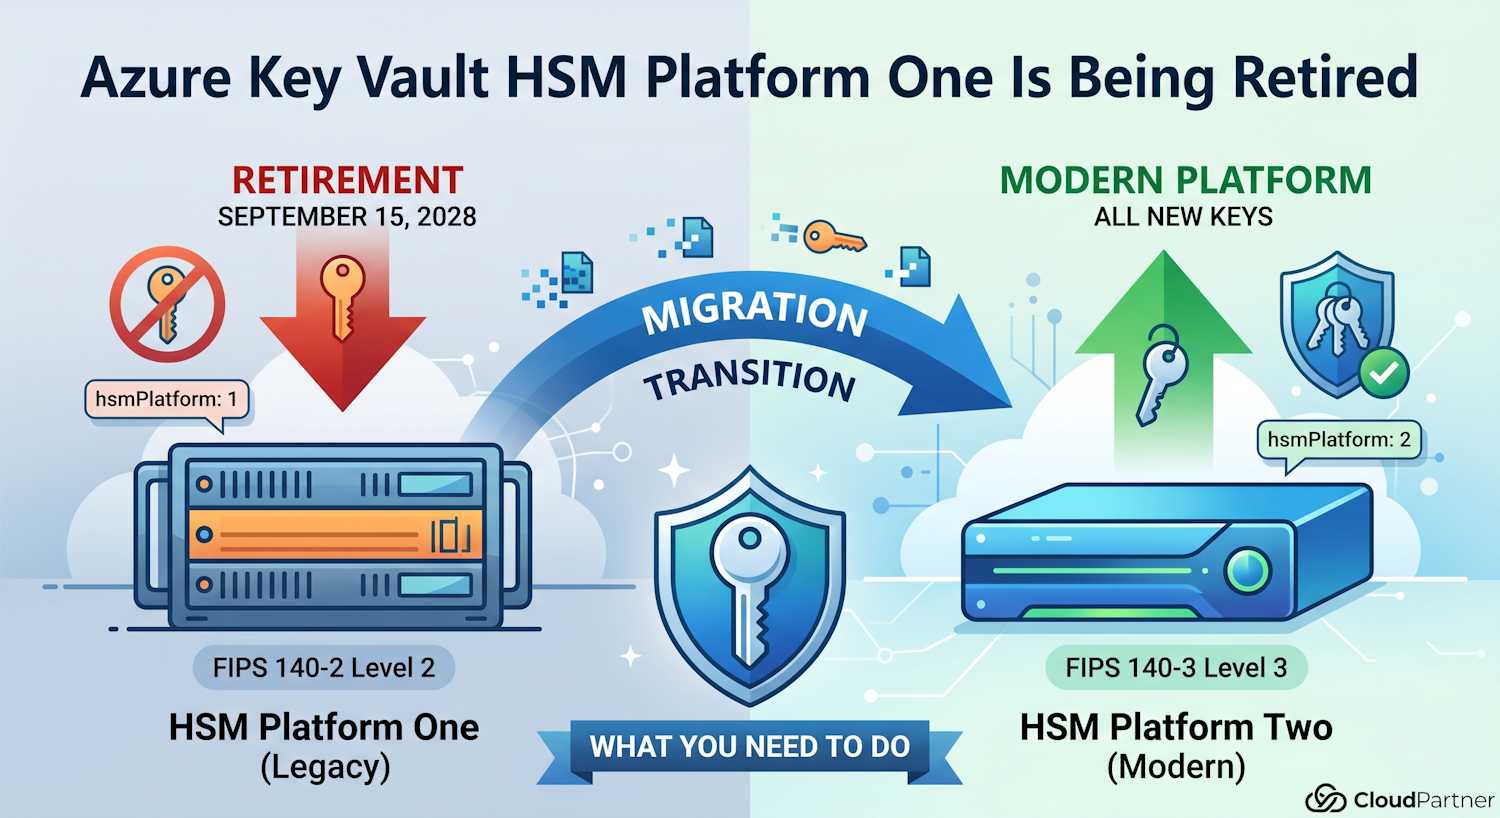
Microsoft is retiring Azure Key Vault HSM Platform One on September 15, 2028. If you're using AKV Premium HSM-protected keys — especially with Microsoft Purview BYOK — here's what it means, how to check your keys, and why waiting until 2028 is a bad idea.
Microsoft Defender integrates with Agent365 to give security teams visibility, threat detection, and real-time protection for AI agents — regardless of which platform built them.