PS HarriJaakkonen :~/Posts> Get-AllPosts | Sort-Object Date -Descending | Format-List
PS> Find-Post
Microsoft Entra Tenant Governance Is GA: What Changed and How to Use It

Microsoft Entra Tenant Governance is generally available. Here is what is GA, what is still preview, how licensing works, and how to roll it out without breaking operations.
Read →
Rethinking Security for the Age of AI: A Practical Enterprise Analysis

A practical analysis of Microsoft's new Cyber Stack vision for AI-era defense, with concrete guidance for identity, DevOps, governance, and SOC operations.

Read →
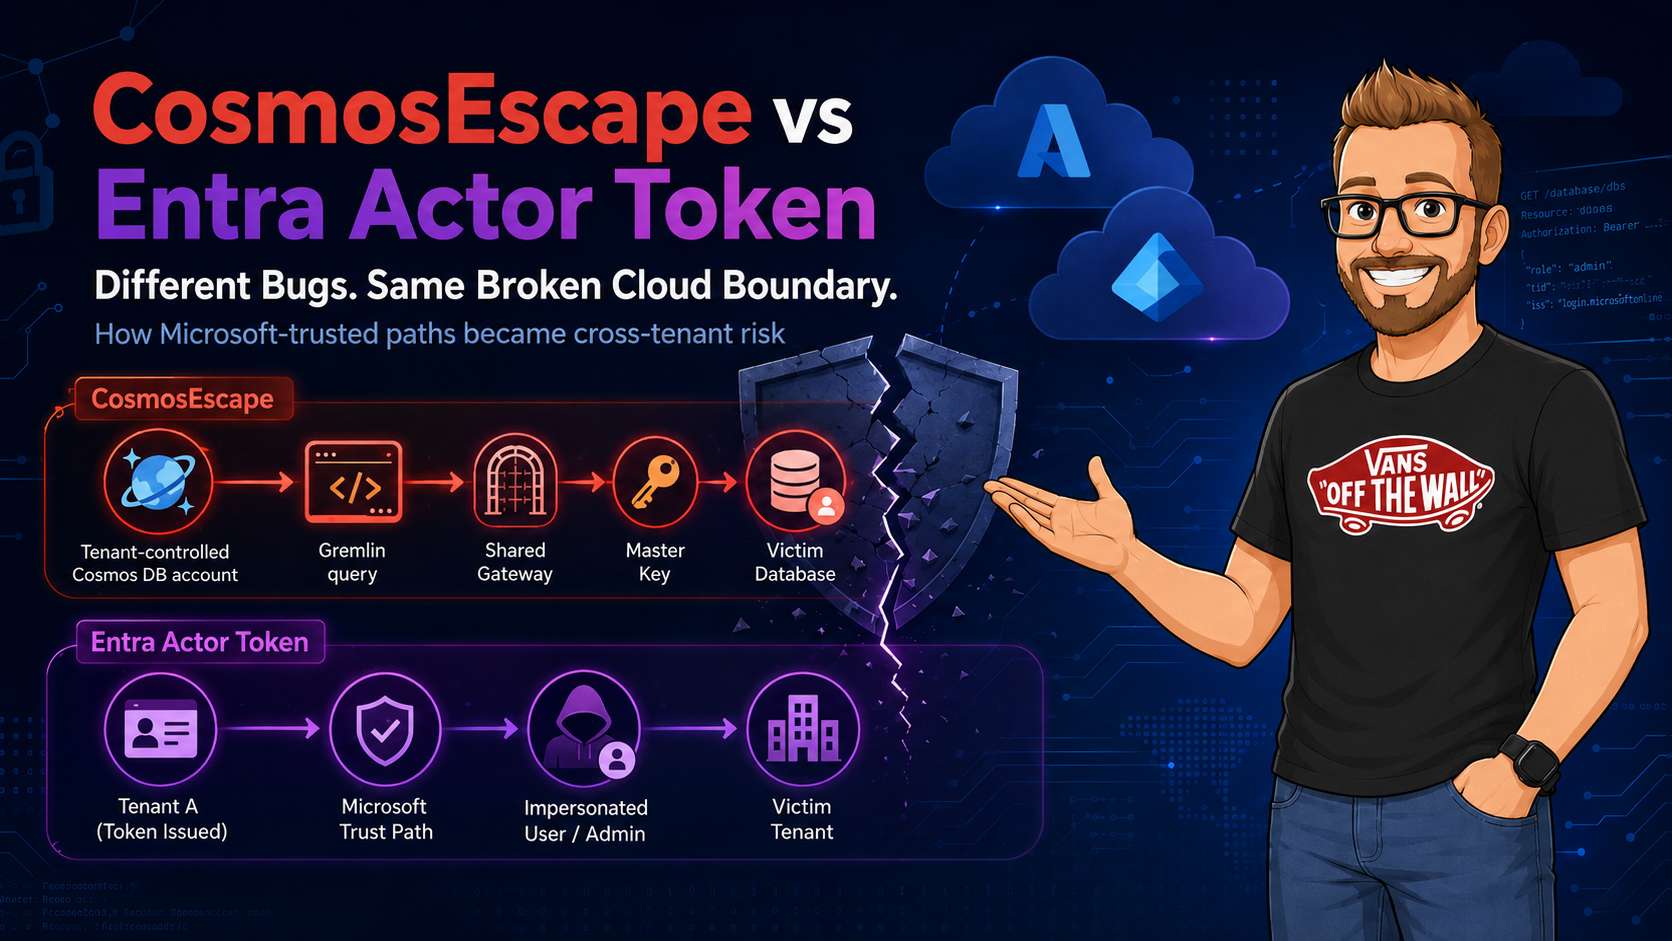
CosmosEscape and the Entra Actor Token Vulnerability: Different Bugs, Same Broken Cloud Boundary

A technical comparison of CosmosEscape and CVE-2025-55241, showing how different exploit chains can fail on the same tenant-boundary control in cloud platforms.

Read →
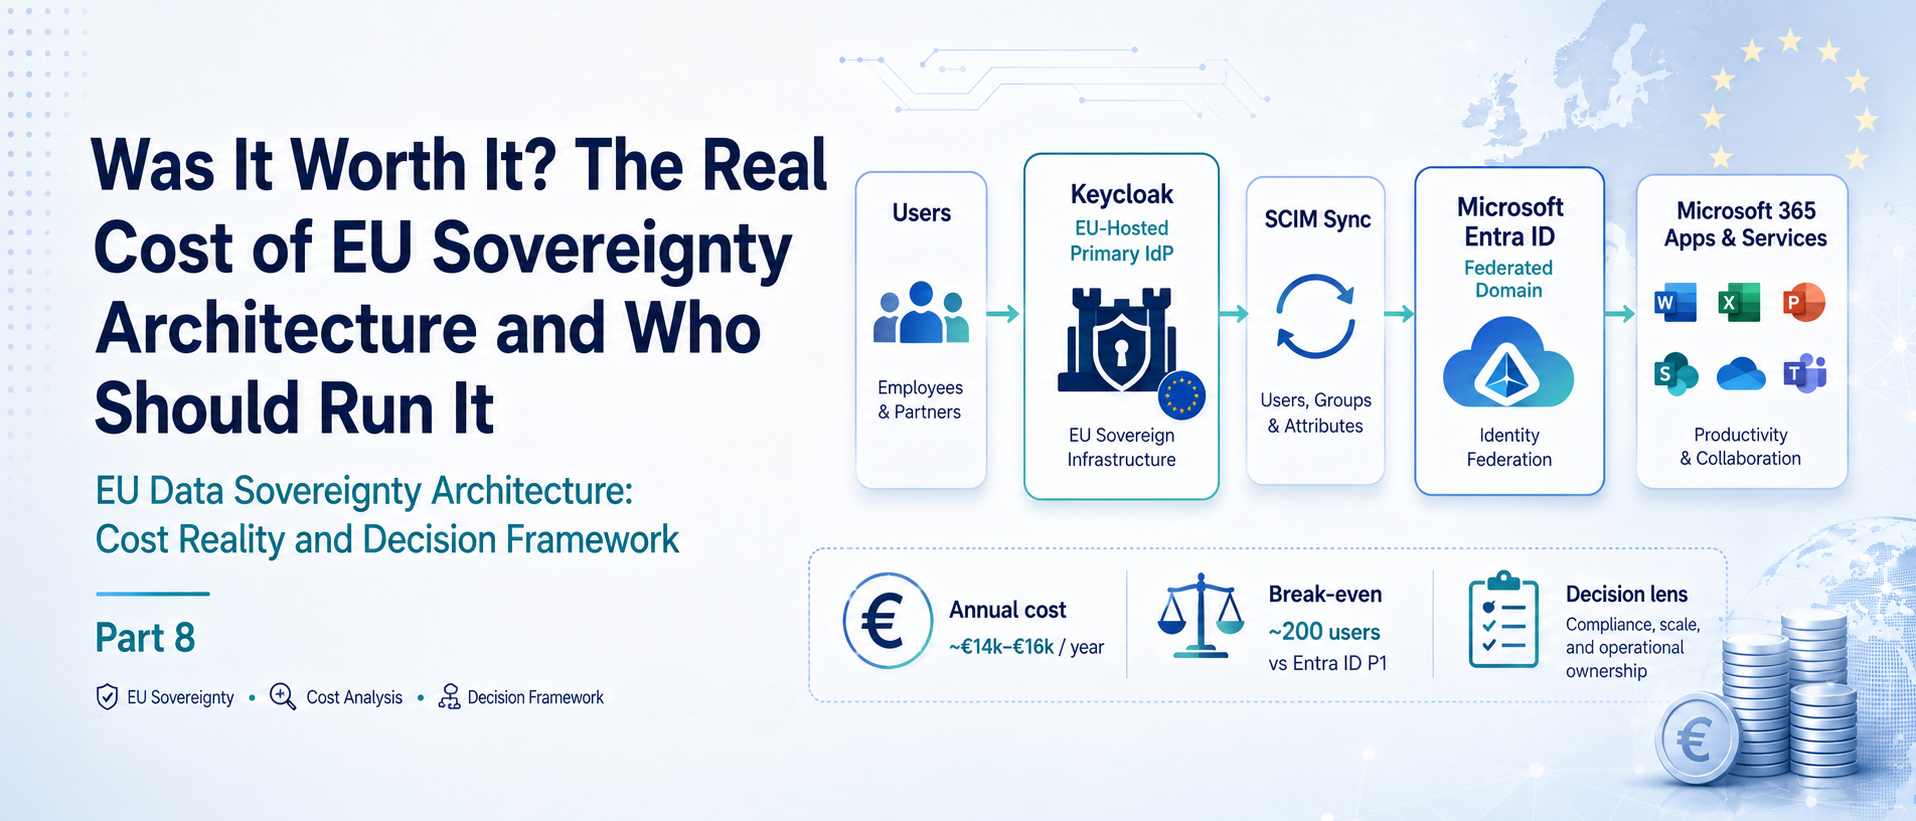
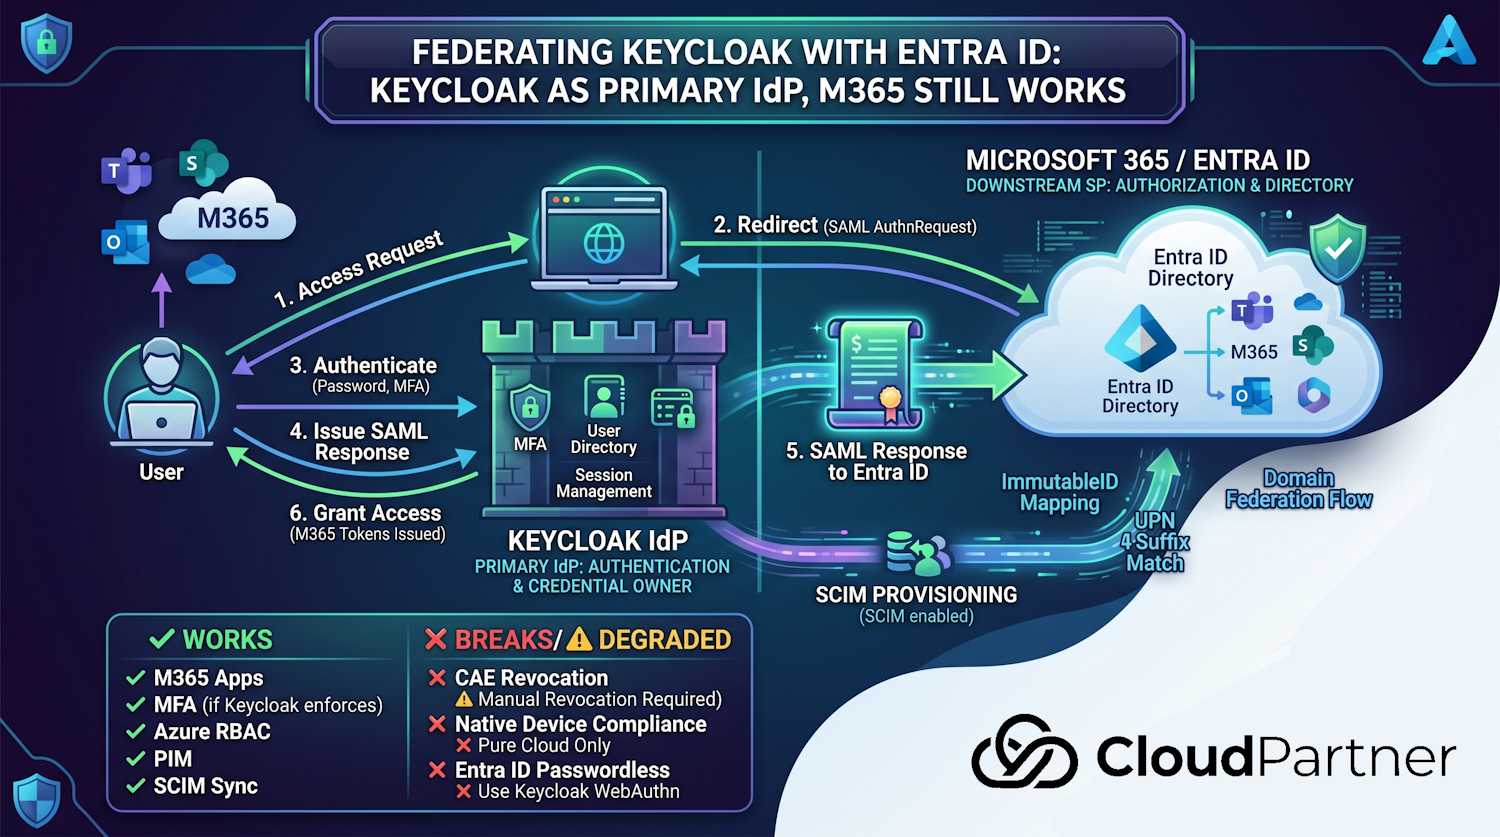
Was It Worth It? The Real Cost of EU Sovereignty Architecture and Who Should Run It — Part 8

Part 8 of the EU data sovereignty series. An honest cost and complexity analysis of the Keycloak–Entra ID federation architecture: infrastructure costs, operational overhead, comparison to native Entra ID licensing, and a practical decision framework for which organisations genuinely need this.

Read →
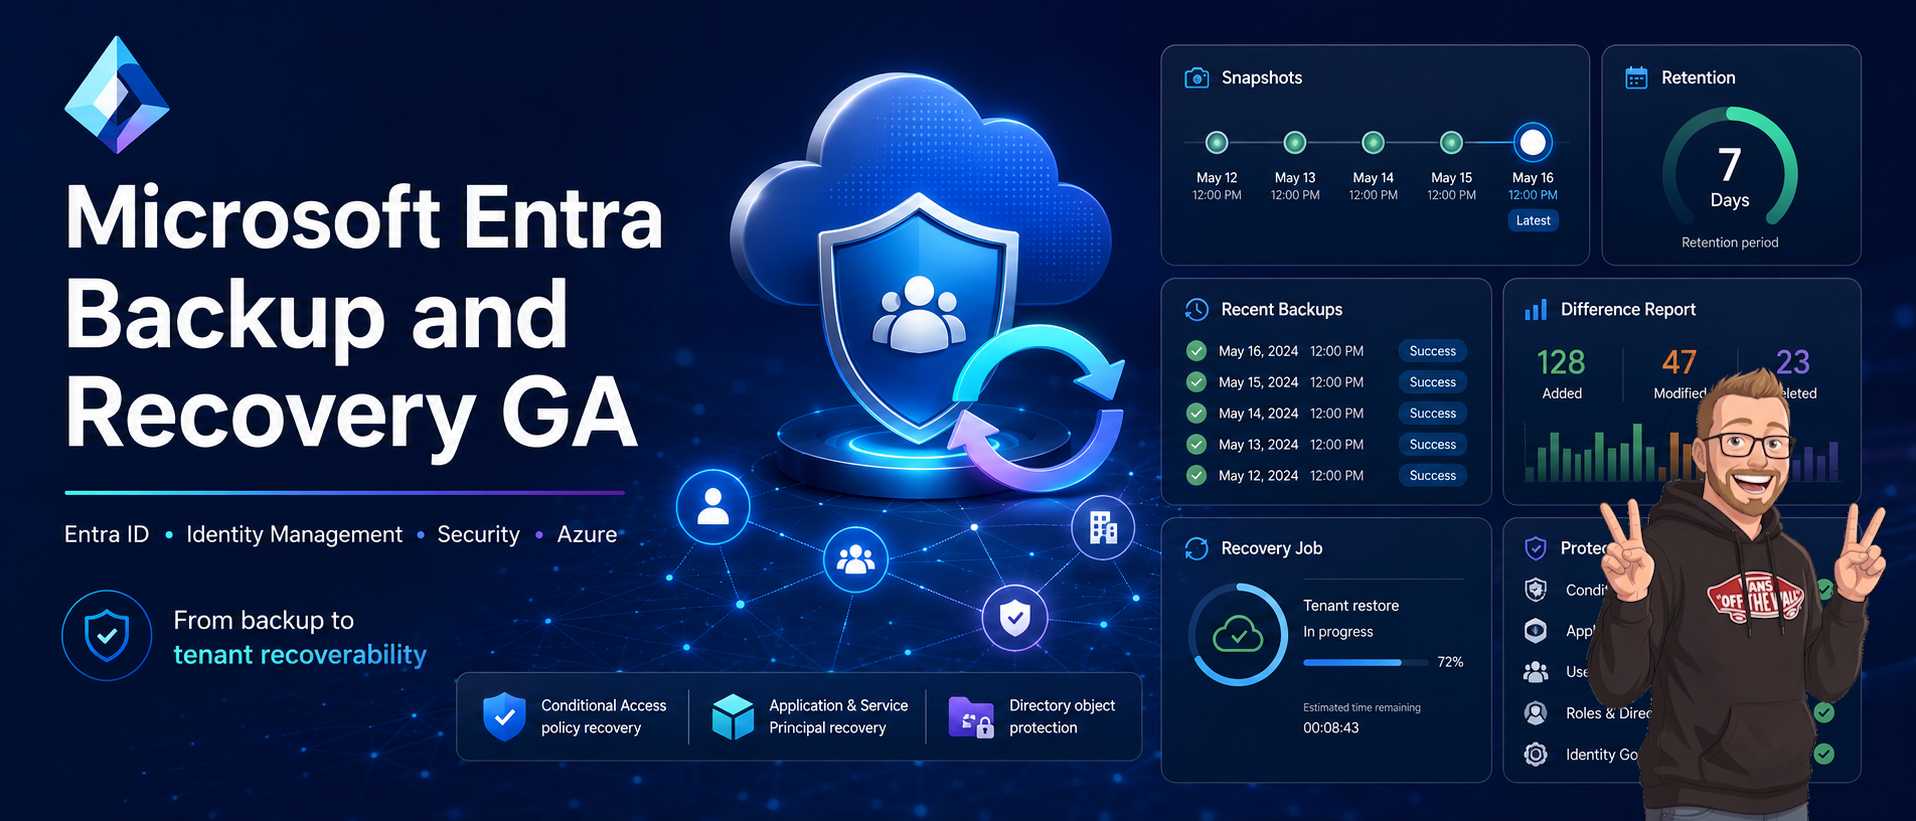
Microsoft Entra Backup and Recovery GA

A draft on Microsoft Entra Backup and Recovery going generally available, why tenant recoverability matters, and how to treat backup as one layer in a broader recovery plan.

Read →
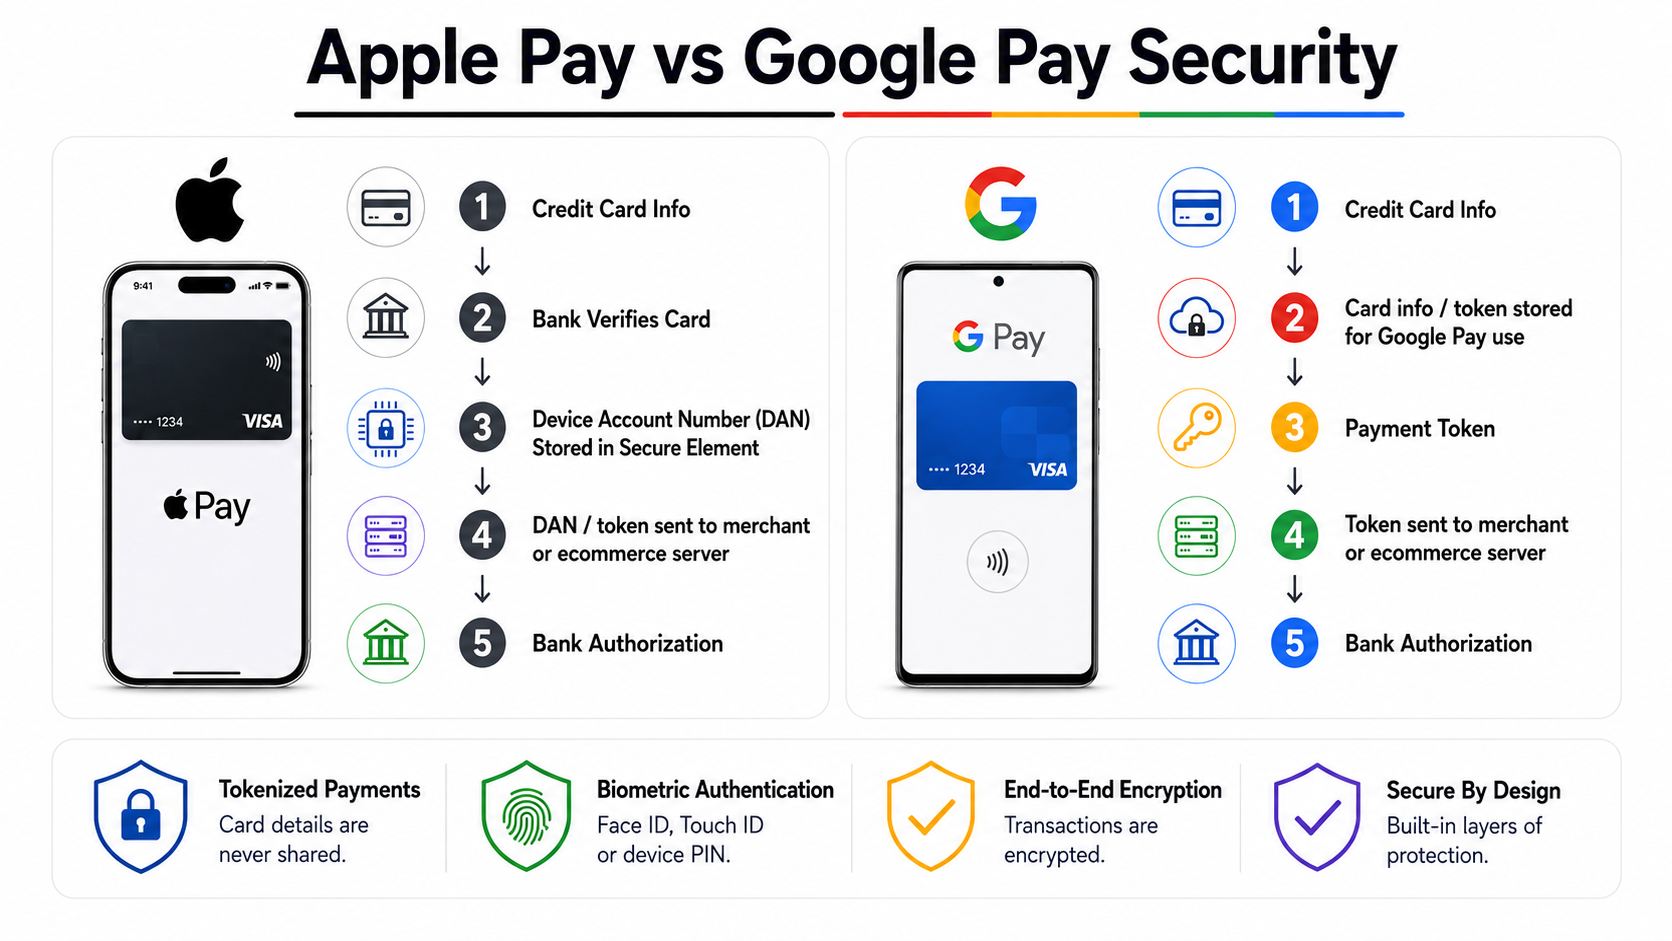
Apple Pay vs Google Pay: What Security Architects Can Learn About Tokenization and Zero Trust

What Apple Pay and Google Pay teach security architects about tokenization, trust anchors, device-bound assurance, and Zero Trust identity design.

Read →
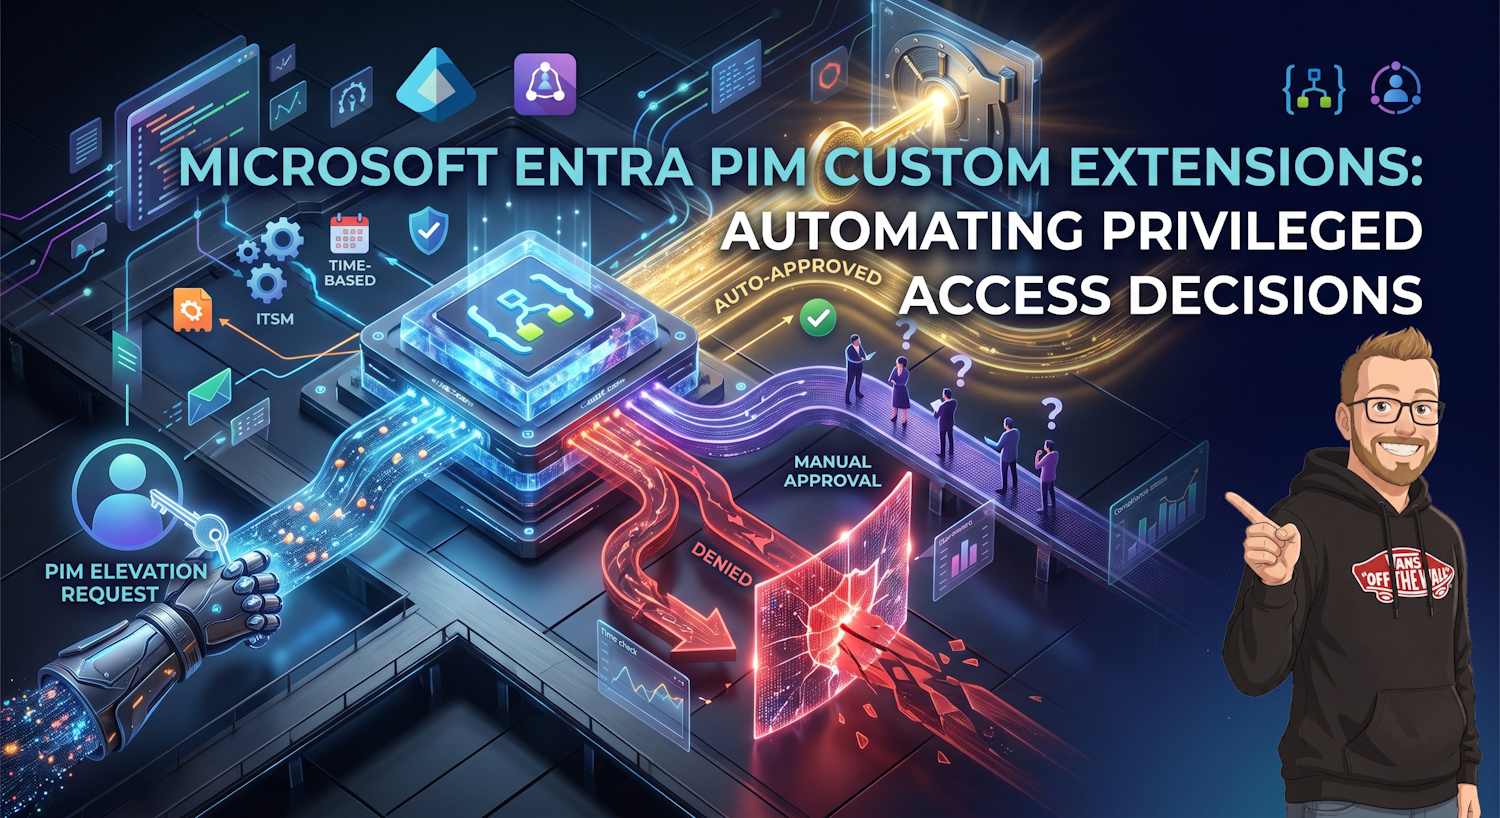
Microsoft Entra PIM Custom Extensions: Automating Privileged Access Decisions

Deep dive into PIM Custom Extensions: automated logic gates for privileged access workflows. How to approve/deny elevation requests based on custom business logic, audit trails, and real-world patterns.

Read →
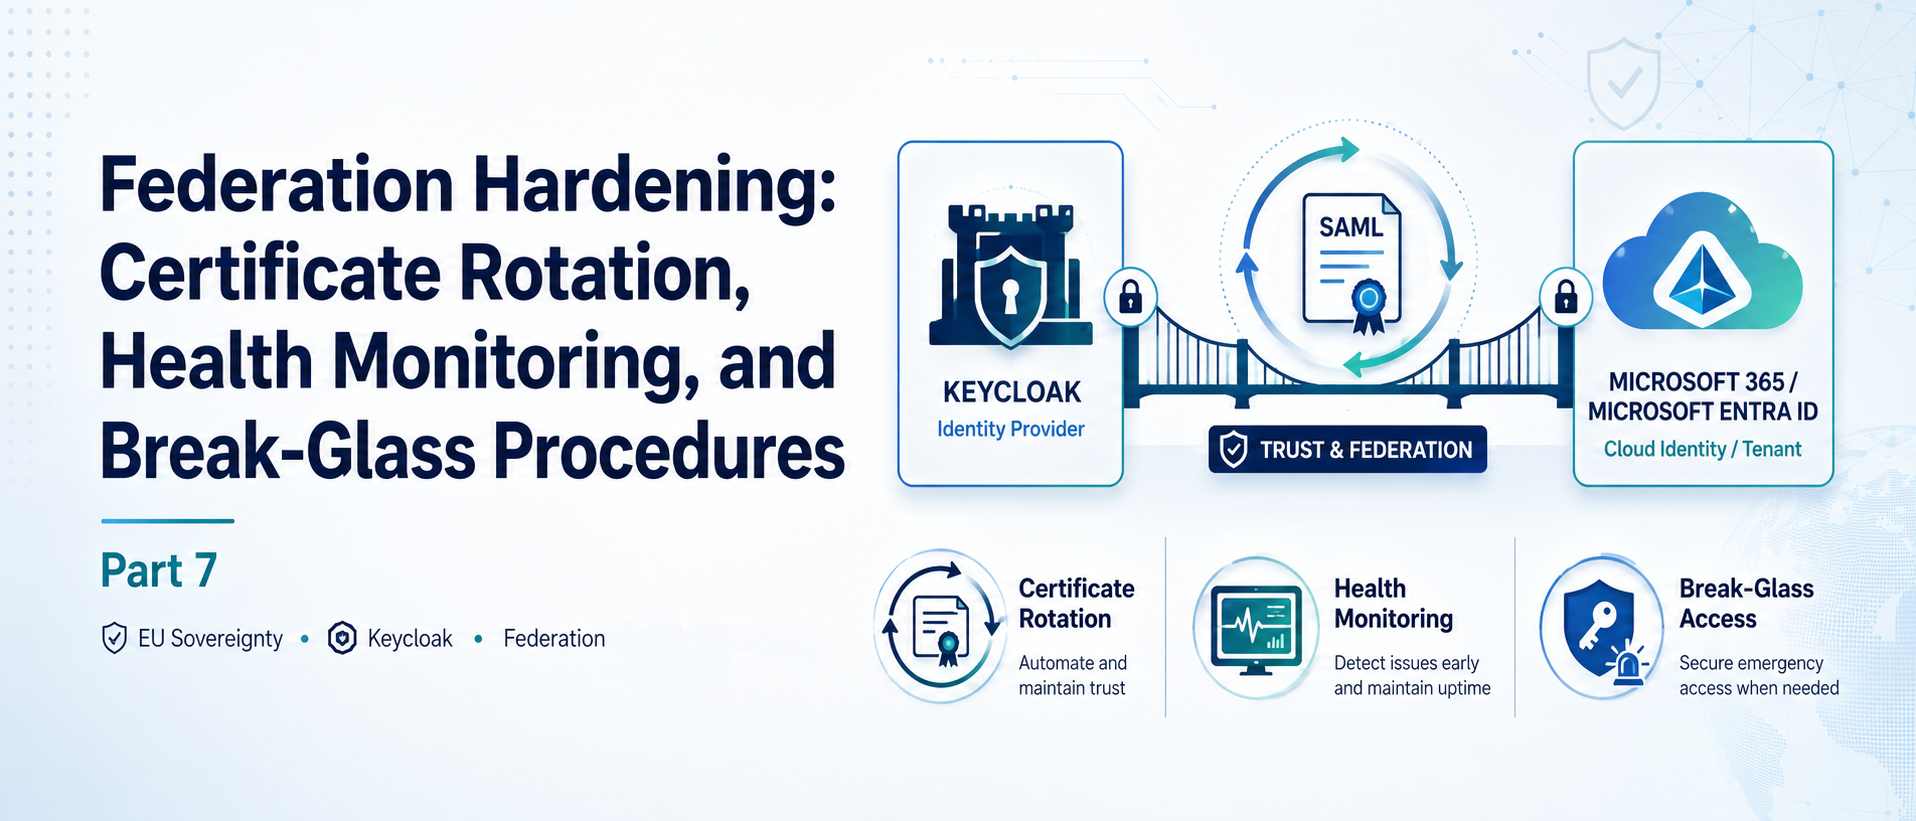
Federation Hardening: Certificate Rotation, Health Monitoring, and Break-Glass Procedures — Part 7

Part 7 of the EU data sovereignty series. How to rotate your Keycloak SAML signing certificate without breaking M365 authentication, monitor federation health, tune Conditional Access under federation, and build a break-glass procedure for Keycloak downtime.

Read →
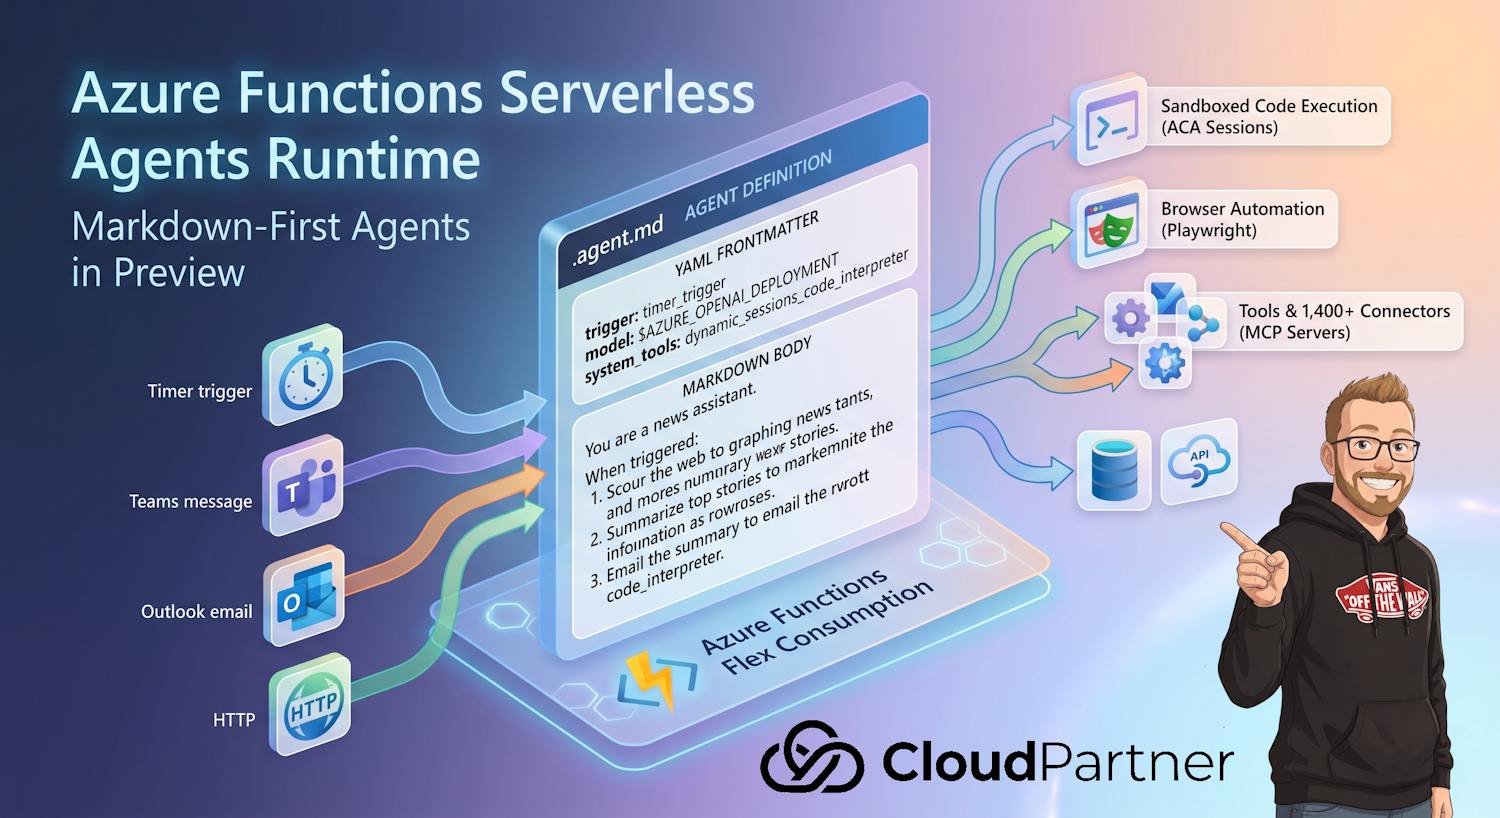
Azure Functions Serverless Agents Runtime: Markdown-First Agents in Preview

Azure Functions now has a serverless agents runtime in public preview: agents defined as .agent.md files, triggered by the same events as Functions, wired to 1,400+ connectors and MCP servers.

Read →
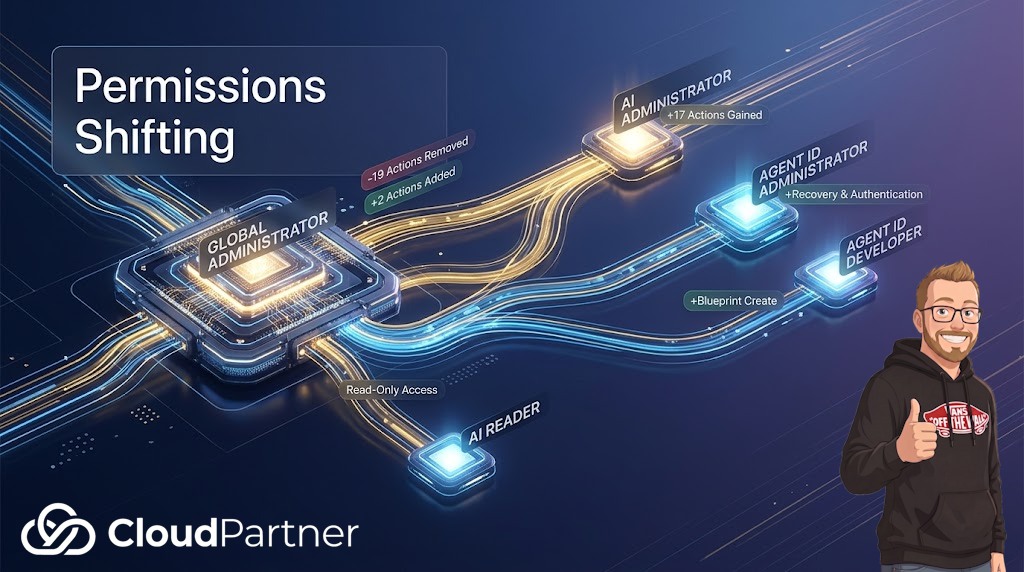
Why Global Administrator Lost Agent User Lifecycle Permissions in Microsoft Entra

Why Microsoft moved Agent ID and agent-user lifecycle permissions away from Global Administrator, which AI and Agent ID roles now own the work, and how to review it in a tenant.

Read →
SCIM Provisioning from Keycloak to Entra ID: Keeping Two Directories in Sync - Part 6

Part 6 of the EU data sovereignty series. How to provision users from Keycloak to Entra ID via SCIM — the ImmutableID anchor problem, attribute mapping for Governance lifecycle workflows, deprovisioning, and handling edge cases.

Read →
AZ-700 Part 1: Exam Overview and Networking Foundations

AZ-700 part 1 covering exam overview, Azure network engineer role, networking prerequisites, and study strategy.

Read →
AZ-700 Part 2: Core Networking - IP, DNS, VNets

AZ-700 core networking study guide covering Azure VNets, subnetting, public IPs, Azure DNS, Private DNS, and DNS Private Resolver.

Read →
AZ-700 Part 3: Routing, NAT, Monitoring, and DDoS

AZ-700 study guide covering VNet peering, UDRs, forced tunneling, Azure Route Server, NAT Gateway, Network Watcher, Azure Monitor, and DDoS Protection.

Read →
AZ-700 Part 4: VPN Connectivity

AZ-700 VPN study guide covering site-to-site VPN, point-to-site VPN, gateway SKUs, IPsec/IKE, certificates, Microsoft Entra ID, and RADIUS authentication.

Read →
AZ-700 Part 5: ExpressRoute and Virtual WAN

AZ-700 study guide covering ExpressRoute circuits, peering, gateways, encryption, BFD, troubleshooting, and Azure Virtual WAN architecture.

Read →
AZ-700 Part 6: Load Balancer, Traffic Manager, and Gateway Load Balancer

AZ-700 application delivery study guide covering Azure Load Balancer, Traffic Manager, Gateway Load Balancer, health probes, NAT rules, and outbound SNAT.

Read →
AZ-700 Part 7: Application Gateway and Azure Front Door

AZ-700 study guide covering Azure Application Gateway, Azure Front Door, TLS, routing, rewrite rules, caching, WAF, and Private Link origins.

Read →
AZ-700 Part 8: Private Link, Private Endpoints, and Service Endpoints

AZ-700 private access study guide covering Azure Private Link service, private endpoints, private DNS integration, on-premises access, and service endpoints.

Read →
AZ-700 Part 9: NSGs, ASGs, Flow Logs, and Bastion

AZ-700 network security study guide covering NSGs, ASGs, virtual network flow logs, IP flow verify, Azure Bastion, and Virtual Network Manager security admin rules.

Read →