Microsoft Entra Tenant Governance is generally available. Here is what is GA, what is still preview, how licensing works, and how to roll it out without breaking operations.
A practical analysis of Microsoft's new Cyber Stack vision for AI-era defense, with concrete guidance for identity, DevOps, governance, and SOC operations.
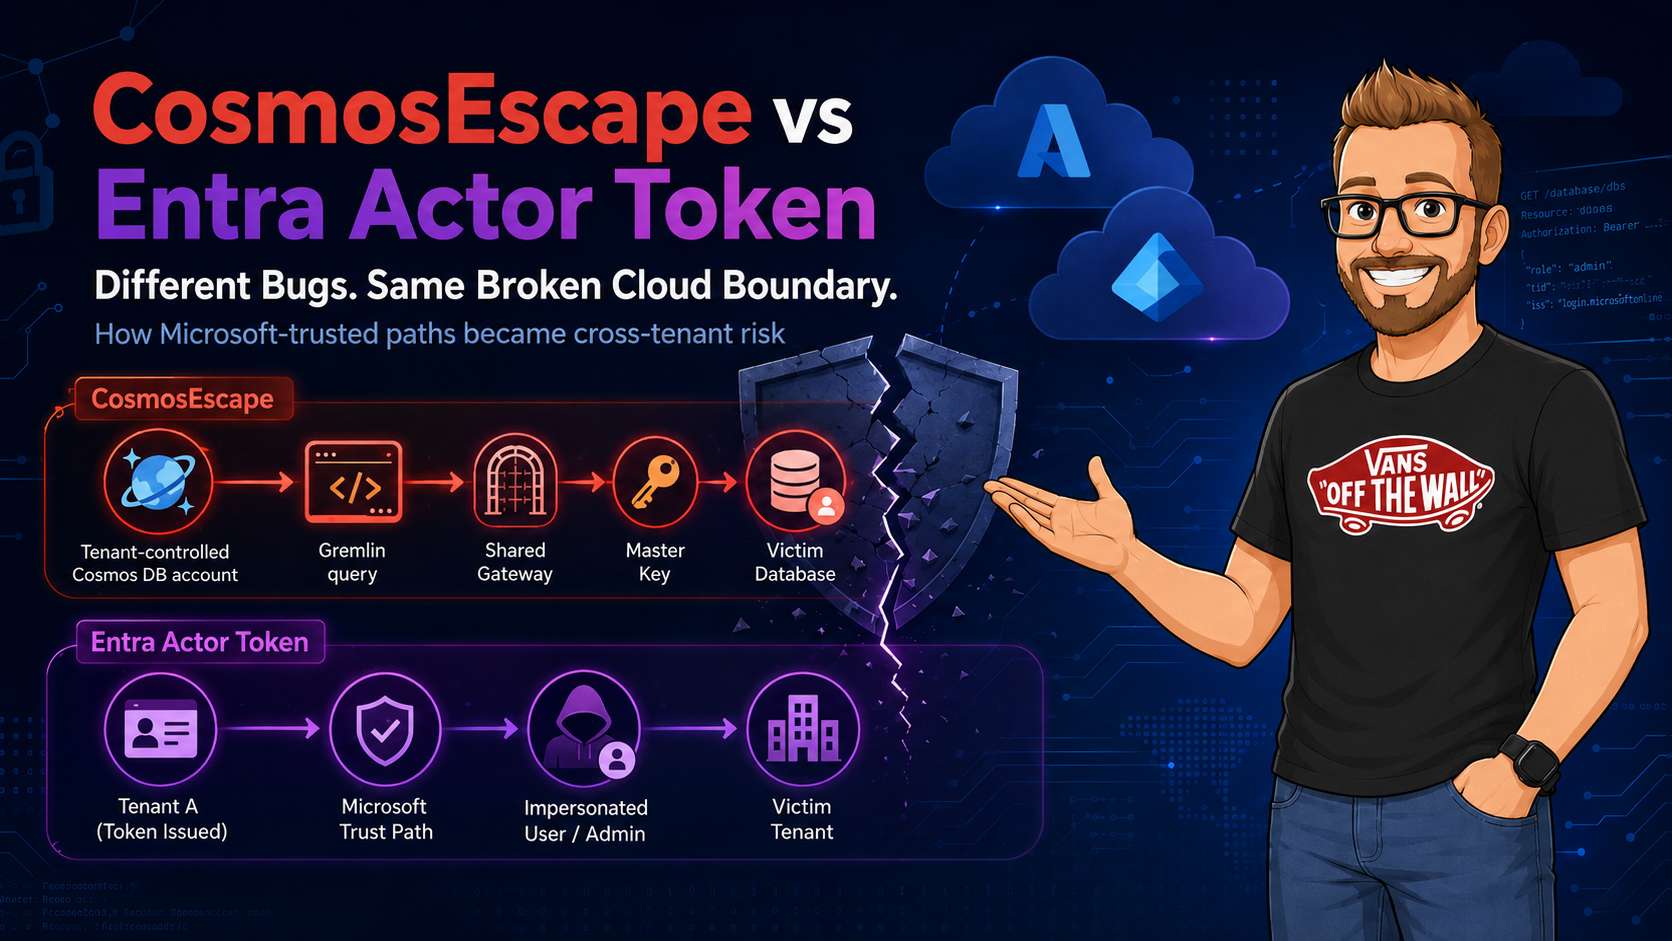
A technical comparison of CosmosEscape and CVE-2025-55241, showing how different exploit chains can fail on the same tenant-boundary control in cloud platforms.
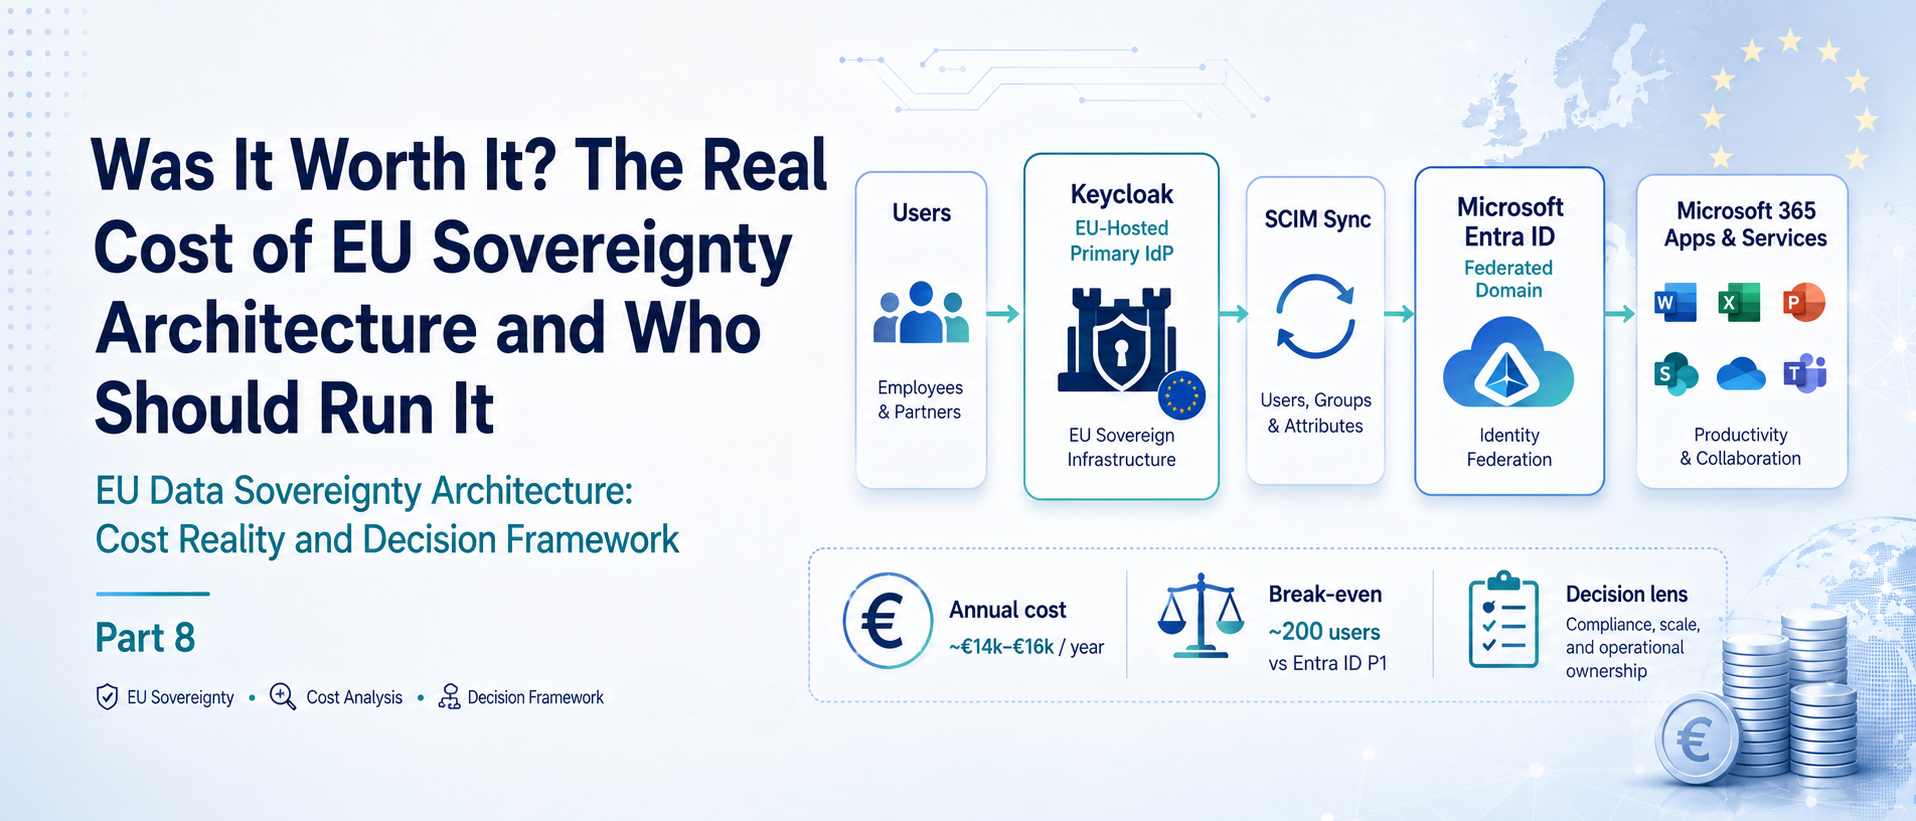
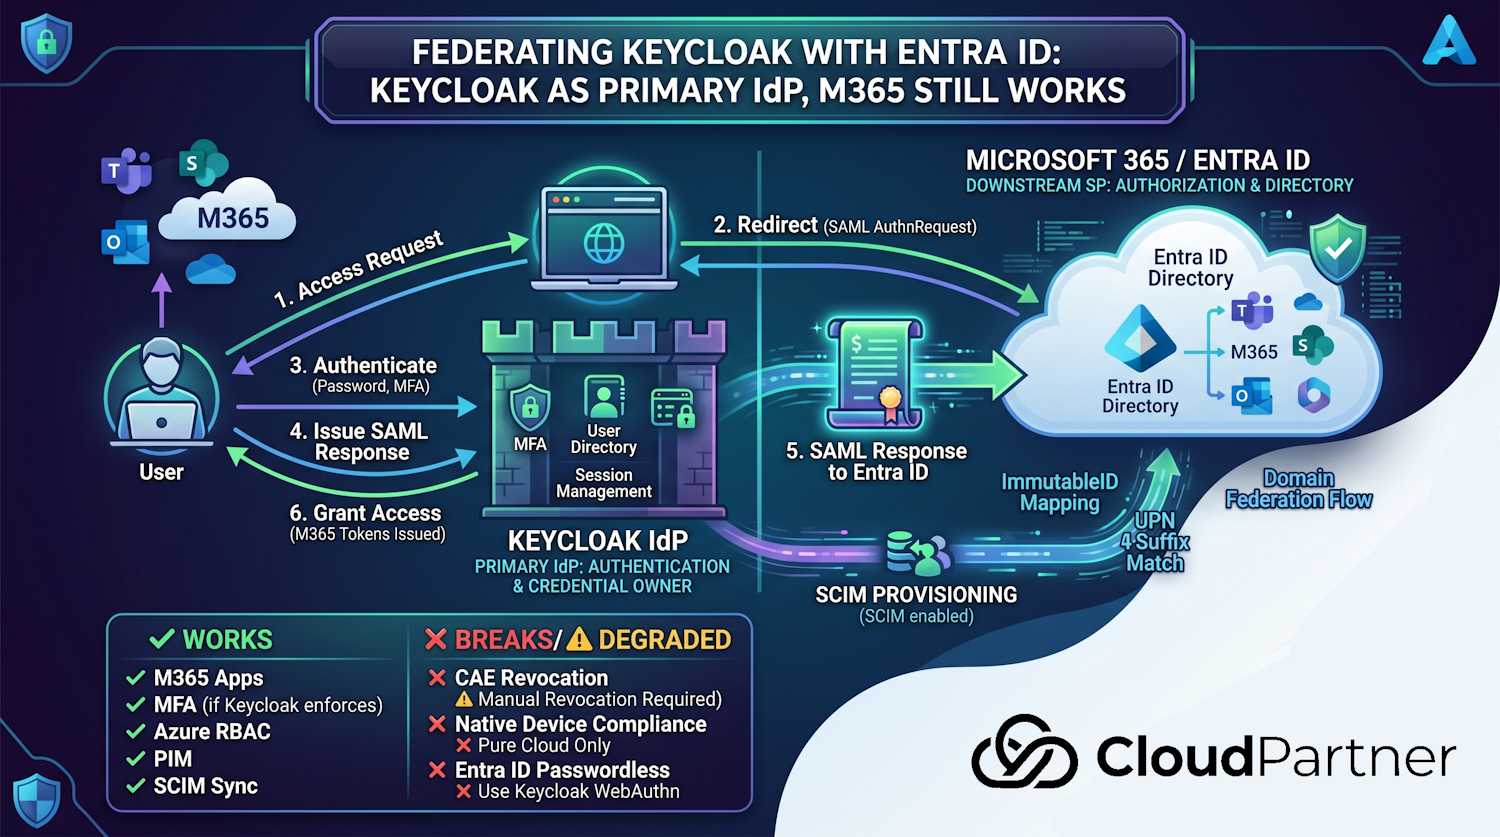
Part 8 of the EU data sovereignty series. An honest cost and complexity analysis of the Keycloak–Entra ID federation architecture: infrastructure costs, operational overhead, comparison to native Entra ID licensing, and a practical decision framework for which organisations genuinely need this.
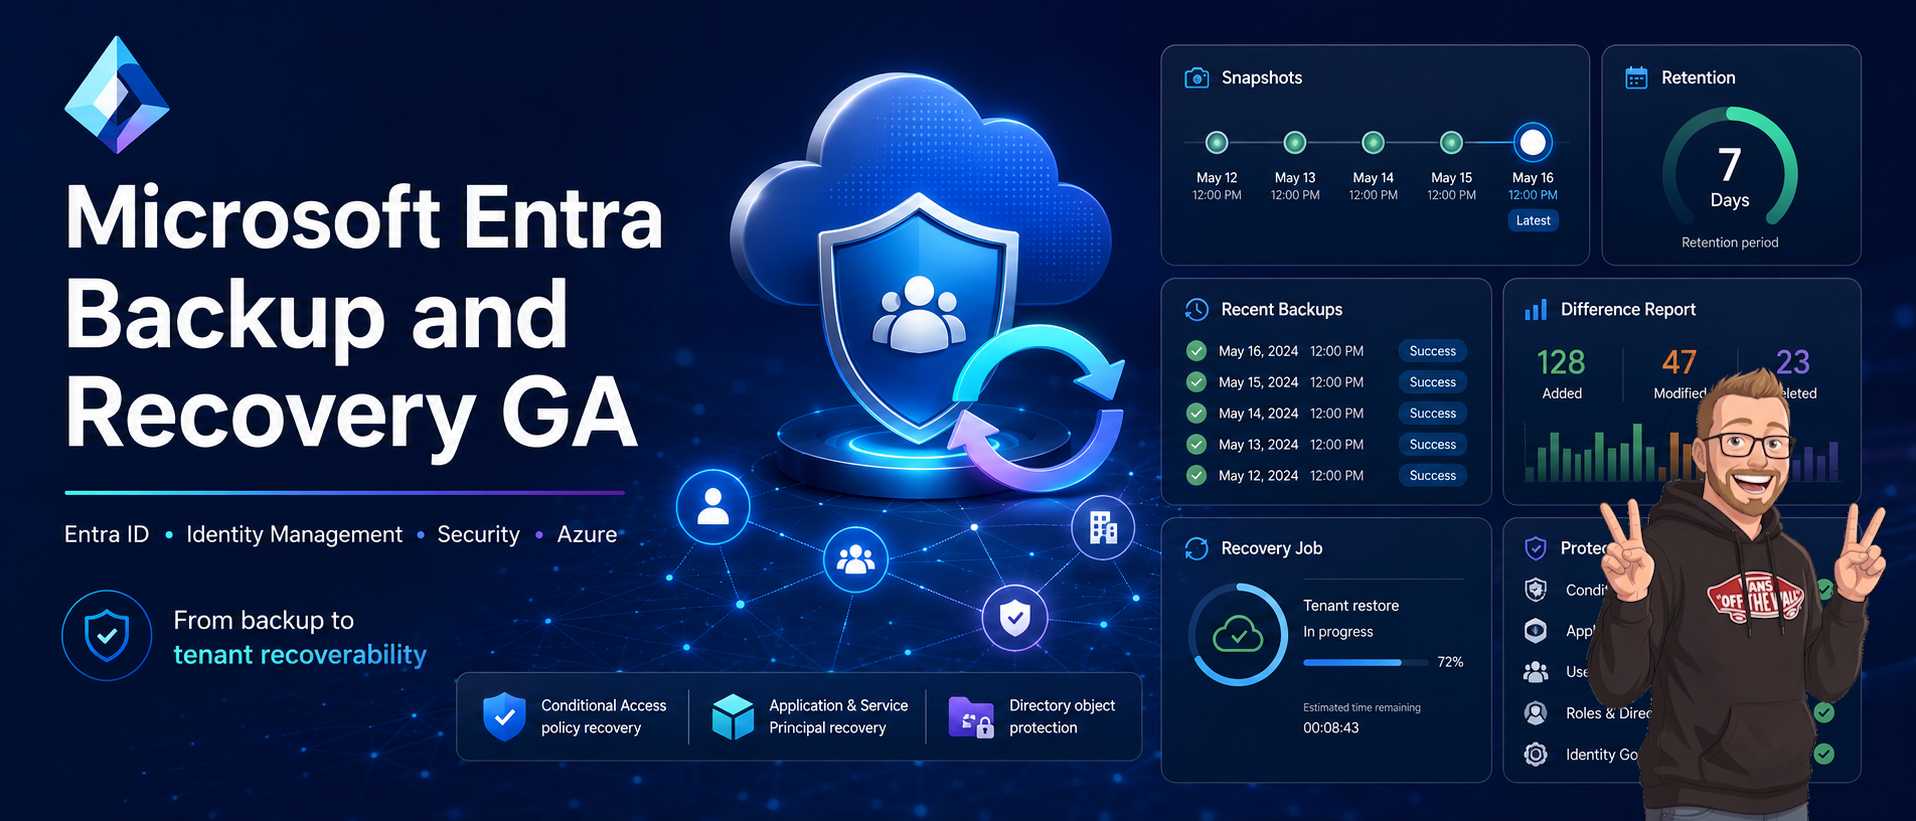
A draft on Microsoft Entra Backup and Recovery going generally available, why tenant recoverability matters, and how to treat backup as one layer in a broader recovery plan.
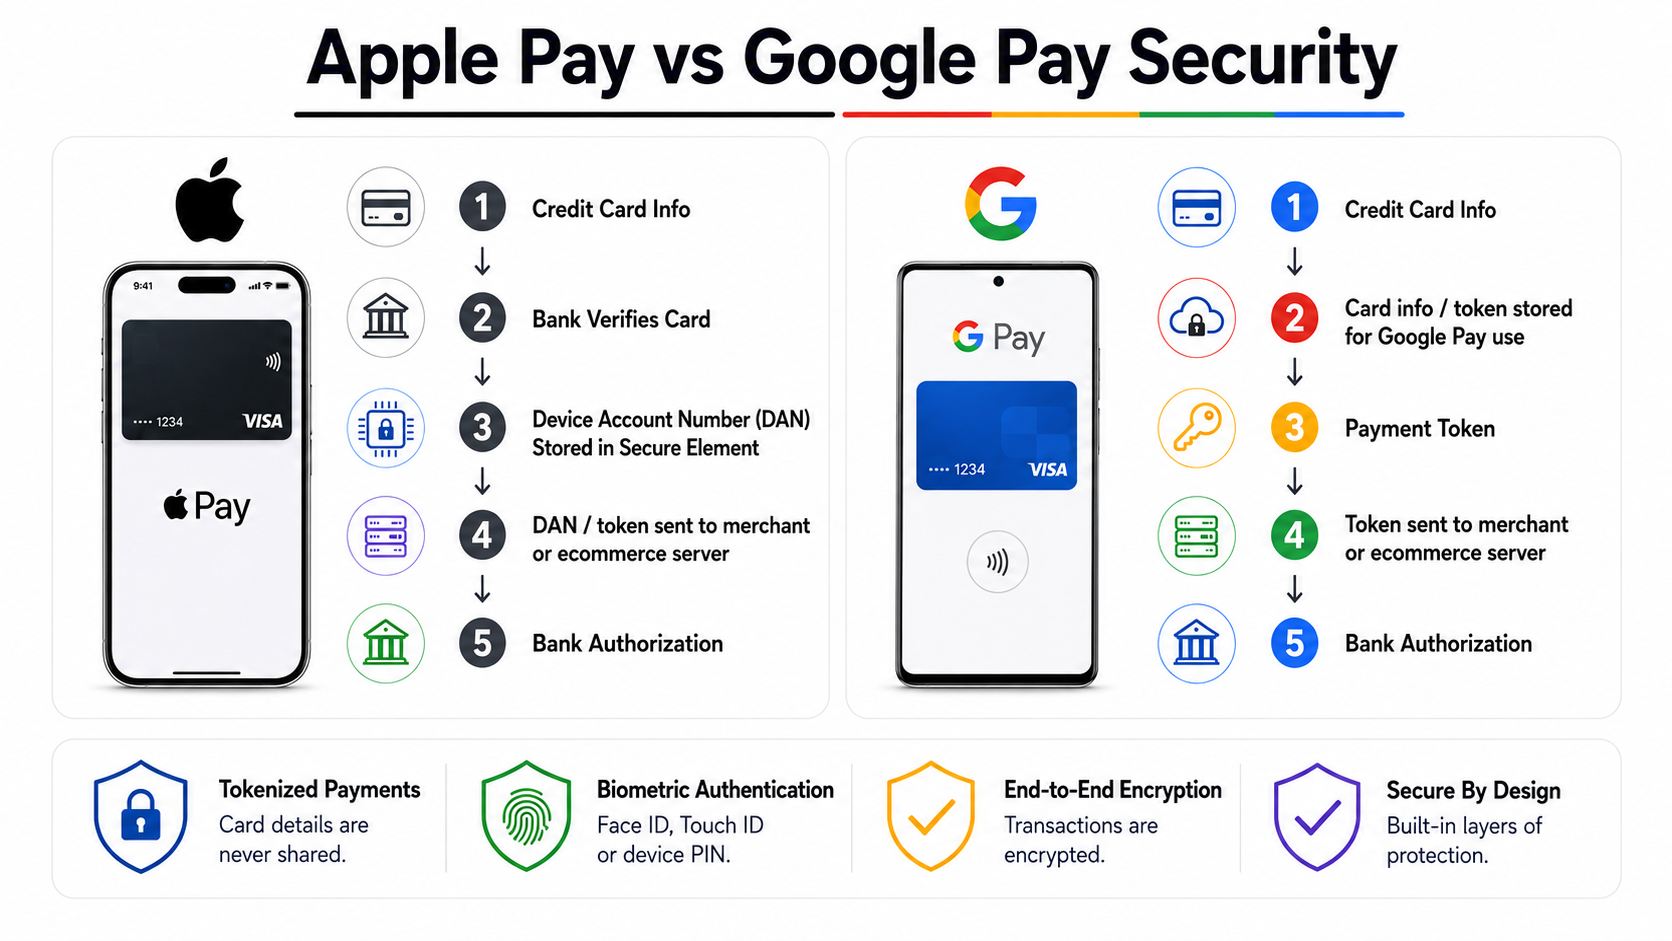
What Apple Pay and Google Pay teach security architects about tokenization, trust anchors, device-bound assurance, and Zero Trust identity design.
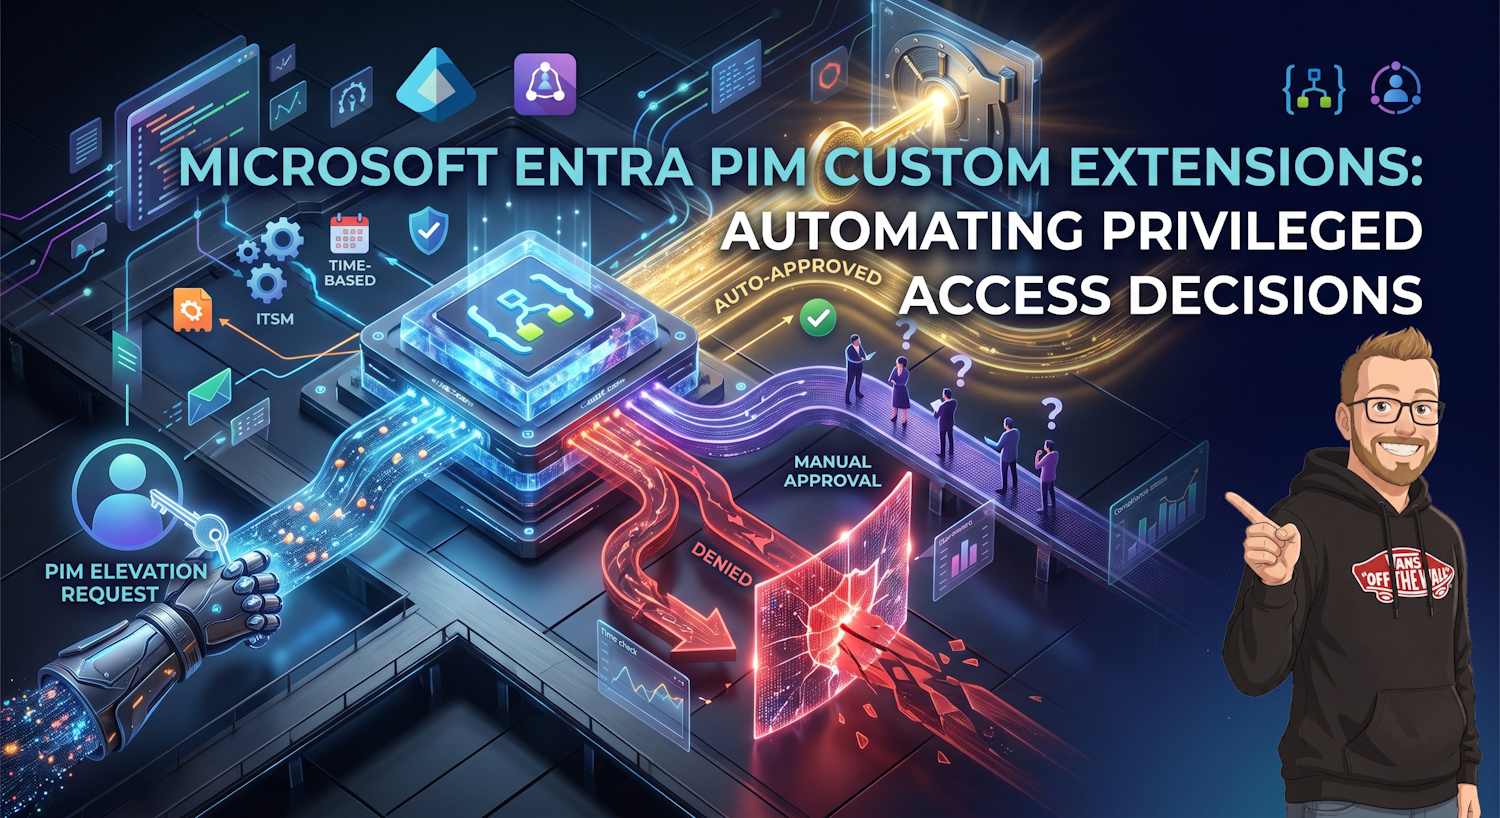
Deep dive into PIM Custom Extensions: automated logic gates for privileged access workflows. How to approve/deny elevation requests based on custom business logic, audit trails, and real-world patterns.
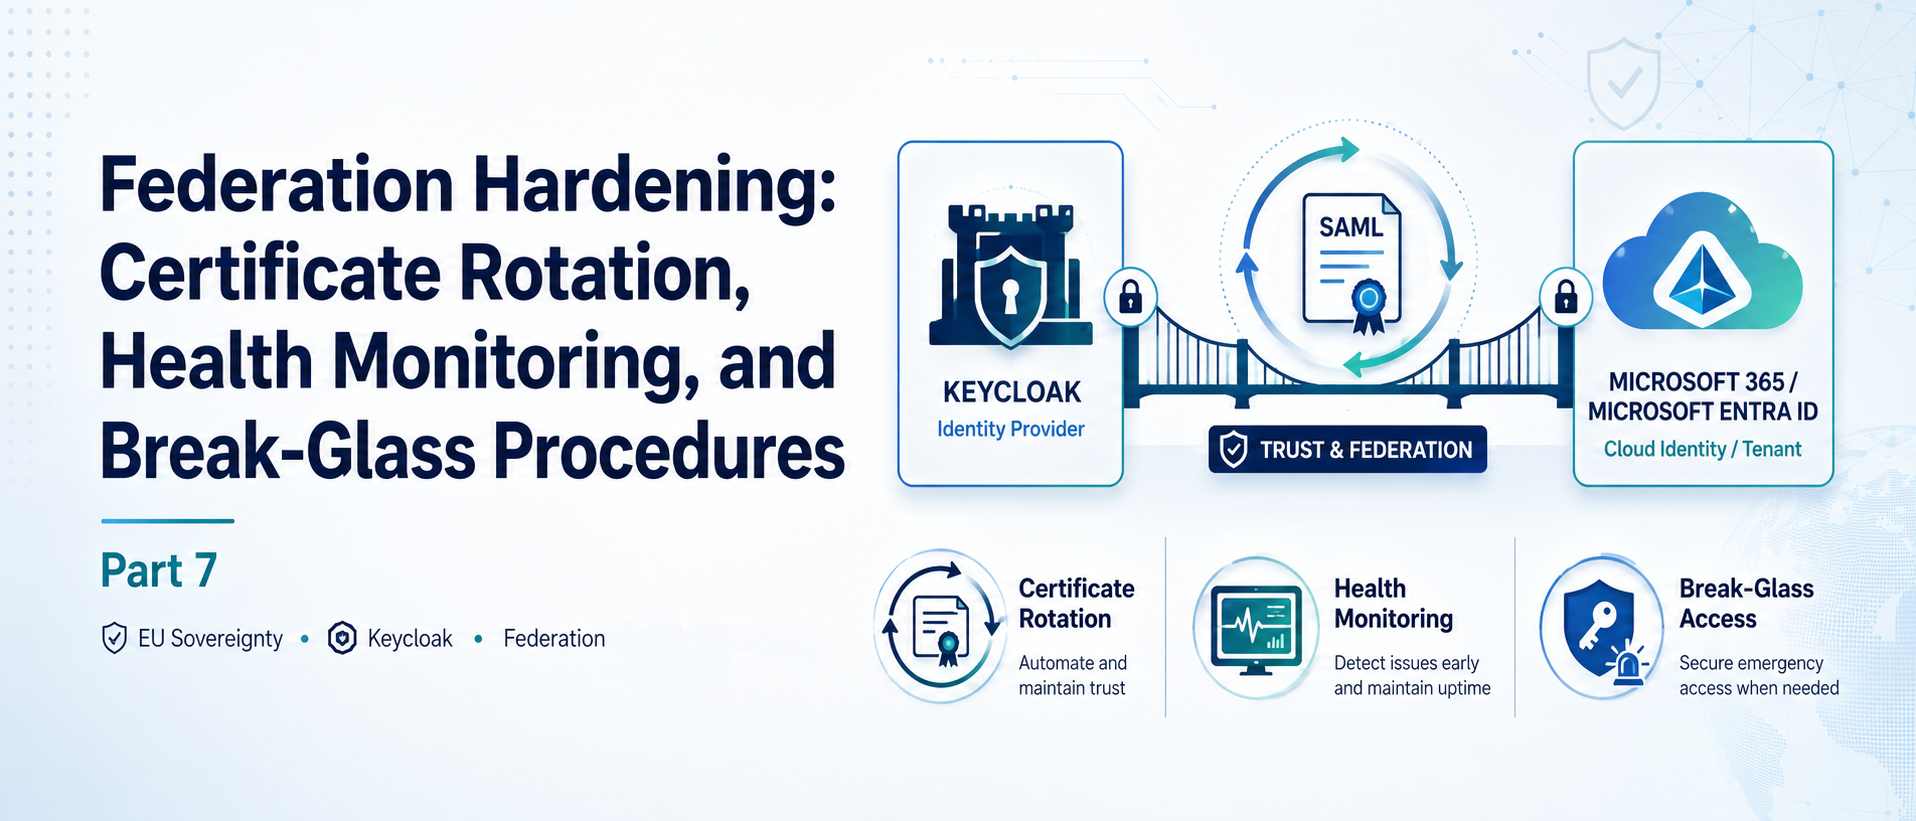
Part 7 of the EU data sovereignty series. How to rotate your Keycloak SAML signing certificate without breaking M365 authentication, monitor federation health, tune Conditional Access under federation, and build a break-glass procedure for Keycloak downtime.
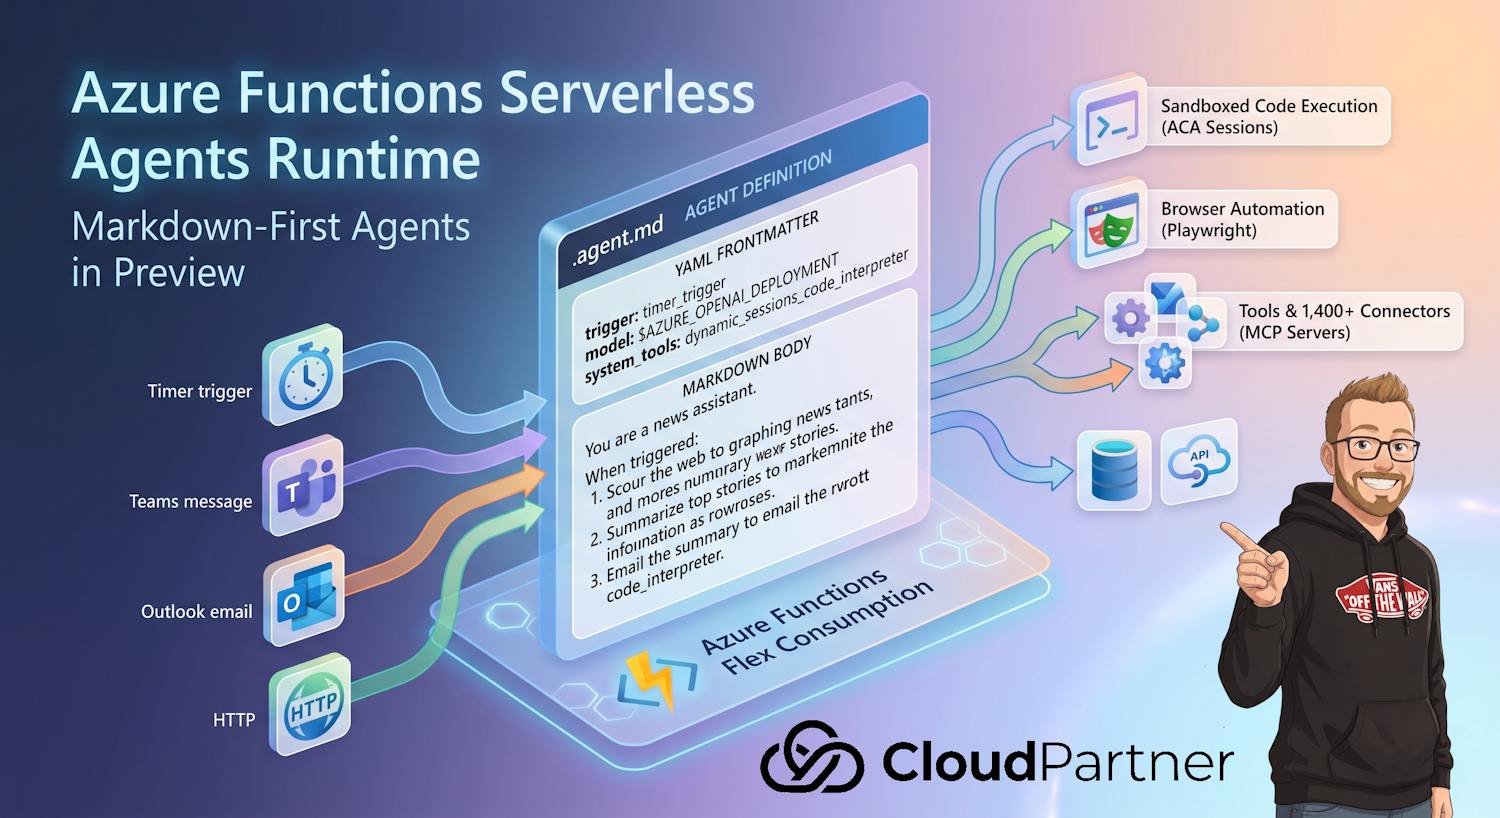
Azure Functions now has a serverless agents runtime in public preview: agents defined as .agent.md files, triggered by the same events as Functions, wired to 1,400+ connectors and MCP servers.
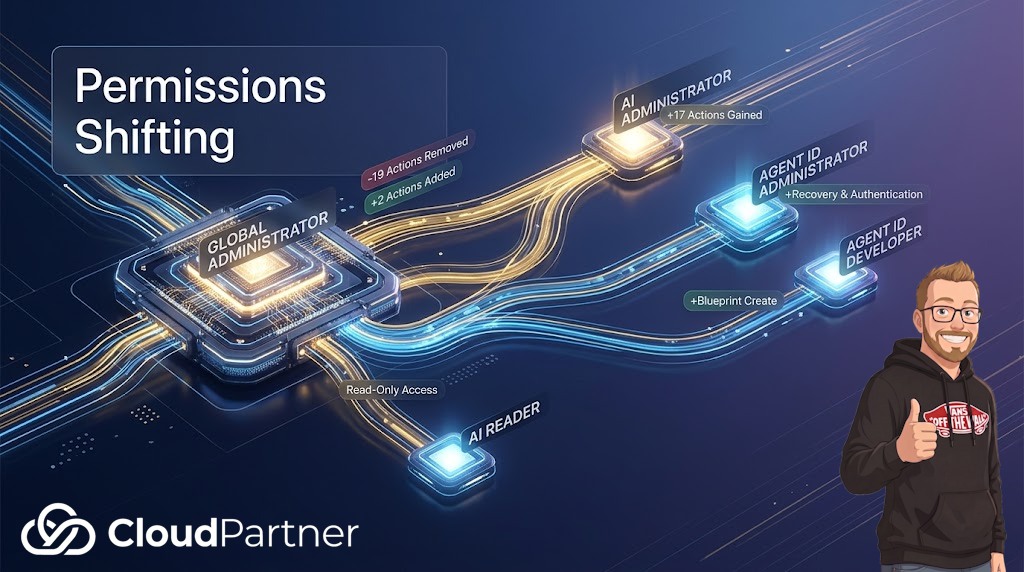
Why Microsoft moved Agent ID and agent-user lifecycle permissions away from Global Administrator, which AI and Agent ID roles now own the work, and how to review it in a tenant.
Part 6 of the EU data sovereignty series. How to provision users from Keycloak to Entra ID via SCIM — the ImmutableID anchor problem, attribute mapping for Governance lifecycle workflows, deprovisioning, and handling edge cases.
AZ-700 part 1 covering exam overview, Azure network engineer role, networking prerequisites, and study strategy.
AZ-700 core networking study guide covering Azure VNets, subnetting, public IPs, Azure DNS, Private DNS, and DNS Private Resolver.
AZ-700 study guide covering VNet peering, UDRs, forced tunneling, Azure Route Server, NAT Gateway, Network Watcher, Azure Monitor, and DDoS Protection.
AZ-700 VPN study guide covering site-to-site VPN, point-to-site VPN, gateway SKUs, IPsec/IKE, certificates, Microsoft Entra ID, and RADIUS authentication.
AZ-700 study guide covering ExpressRoute circuits, peering, gateways, encryption, BFD, troubleshooting, and Azure Virtual WAN architecture.
AZ-700 application delivery study guide covering Azure Load Balancer, Traffic Manager, Gateway Load Balancer, health probes, NAT rules, and outbound SNAT.
AZ-700 study guide covering Azure Application Gateway, Azure Front Door, TLS, routing, rewrite rules, caching, WAF, and Private Link origins.
AZ-700 private access study guide covering Azure Private Link service, private endpoints, private DNS integration, on-premises access, and service endpoints.
AZ-700 network security study guide covering NSGs, ASGs, virtual network flow logs, IP flow verify, Azure Bastion, and Virtual Network Manager security admin rules.