A hands-on look at the Microsoft Entra Resource Policy public preview, with built-in policies, custom Rego, privileged reads, Microsoft Graph simulations, and a safe rollout workflow.
I've been breaking down Microsoft's security stack since before Entra ID was even called Entra ID. No fluff, no paywalls — just technical depth on Entra, Sentinel, Defender, Purview, and Azure Security that the official docs rarely give you.
If you find these articles useful, you can support my work through Stripe.
Contribute via Stripe
Discussion on technical topics and MVP path exploration. Pick the intensity that fits your timeline. Only for Individuals.
A hands-on look at the Microsoft Entra Resource Policy public preview, with built-in policies, custom Rego, privileged reads, Microsoft Graph simulations, and a safe rollout workflow.
Microsoft Entra is extending identity verification from account recovery to passkey onboarding and Conditional Access step-up. Here is what Ignite 2026 announced and how the journeys differ.
Microsoft Agent 365 Ignite updates cover agent identity, governance, activity export, local-agent security, risk, multi-tenant management and AI cost insights.
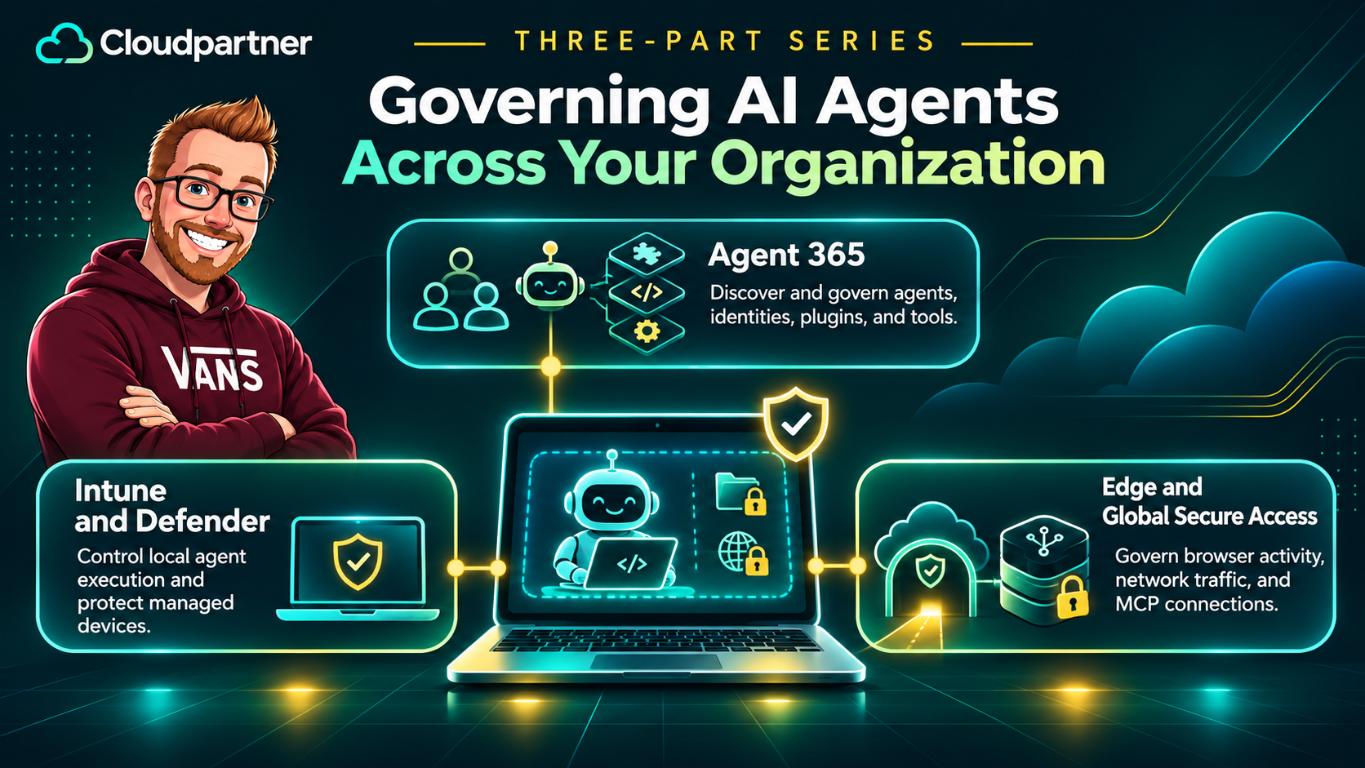
Compare Intune governance, Defender runtime inspection, and Windows process container restrictions for local AI agents.
Compare Edge managed-agent browsing and extension controls with Global Secure Access agent traffic, MCP policy and Purview DLP.
How Every time strict works in Microsoft Entra Conditional Access, why it is not a 10-second timer, and where Private Access and PIM fit.
Windows 365 for Agents was already generally available before Ignite 2026. The update adds Copilot Credits eligibility, new Copilot Studio and Foundry paths, on-premises access with agent identities, and persistent Cloud PCs in private preview.